 Do Son
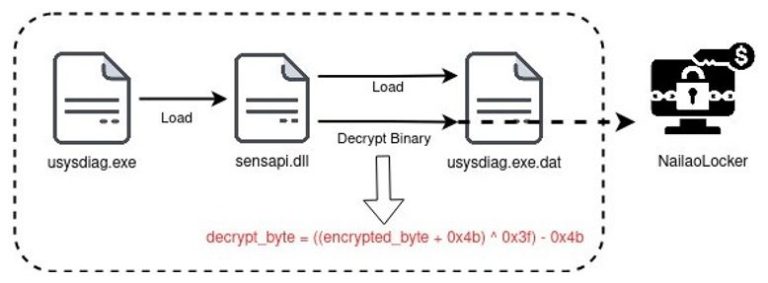
FortiGuard Labs unveils NailaoLocker, a new ransomware using Chinese SM2 encryption and a built-in, non-functional decryptor, suggesting a prototype or decoy.
encryption

A new ransomware, KAWA4096, combines features from Qilin and Akira, targeting organizations in the US and Japan with multi-threaded encryption and anti-recovery measures.

According to a report by The Verge, Nintendo has implemented a proprietary encryption mechanism and specialized chip...

Dire Wolf, a new Golang ransomware, is targeting manufacturing/tech in 11 countries. It uses double extortion, deletes backups, and has a "wipe mode" that permanently destroys files.

The U.S. House of Representatives has banned WhatsApp on government devices, citing security and transparency concerns. Meta strongly disputes the "high-risk" assessment.

Anubis, a new RaaS, combines ECIES encryption with a "wipe mode" that permanently destroys files. It's actively targeting healthcare, construction, and engineering sectors.

Spectra Ransomware, an evolution of Chaos, encrypts Windows files with AES-RSA, demands $5,000 in Bitcoin, and uses double extortion tactics with system evasion


A new ransomware strain, Lyrix, targets Windows systems with strong encryption, anti-analysis, and data destruction techniques. Learn how to protect your data.

A Ghostscript vulnerability (CVE-2025-48708) embeds plaintext passwords in encrypted PDF files, undermining document security. Update now!

A critical OpenPGP.js flaw (CVE-2025-47934) allows attackers to spoof message signatures and manipulate content. Update to fix this risk.

Stay ahead in 2025 with top API security best practices for security teams—covering auth, rate limiting, encryption, and threat detection.

Telegram rejects France's request for a backdoor to access private messages, citing security risks. CEO Durov prioritizes privacy over market share.