 Do Son
Microsoft will block MSIX and MSIXBundle attachments in Outlook and Exchange Online starting November 2026 to prevent malware distribution.
Exchange Online
A Microsoft 365 RejectDirectSend bypass lets attackers spoof internal emails. Learn how this RejectDirectSend bypass works and how to protect your tenant.
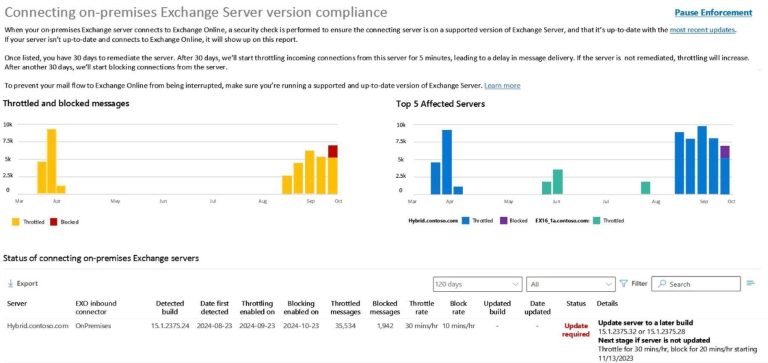
Exchange Online blocking of outdated Exchange 2016 and 2019 servers begins in September 2026, requiring the October 2025 update baseline.

Microsoft warns of a critical flaw (CVE-2025-53786) in Exchange hybrid environments, allowing attackers with on-prem admin access to escalate privileges in Exchange Online.

Datadog reveals a method to impersonate any hybrid Entra ID user, including Global Admins, by exploiting Office 365 Exchange Online service principal. Microsoft calls it "expected behavior."

Varonis uncovers a widespread phishing campaign abusing Microsoft 365's Direct Send, spoofing internal users to bypass email security and harvest credentials.

Enhance email security with Inbound SMTP DANE and DNSSEC. Learn how Microsoft's Exchange Online protects against sophisticated cyberattacks.