 Do Son
The ClingSTUN backdoor hijacks unpatched IoT devices and hides in traffic to public STUN servers. Learn how it spreads and how to stop it.
FortiGuard Labs
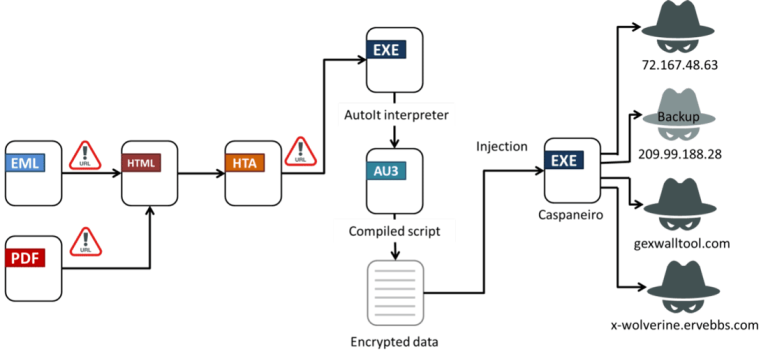
A new Casbaneiro banking trojan campaign hits Latin America. Learn how the Casbaneiro banking trojan evades detection and targets bank logins.

QuickFox supply chain attack trojanizes a VPN app to deploy the FDMTP implant on Windows users. FortiGuard Labs ties it to Twill Typhoon.
FortiGuard Labs found a TrickBot DNS tunneling variant that hides malware C2 communication inside malformed DNS queries and IP address responses.
A global phishing campaign hides a low-detection Lua loader inside fake .ttf font files to drop Remcos, XWorm, Agent Tesla, and a Snake Keylogger.
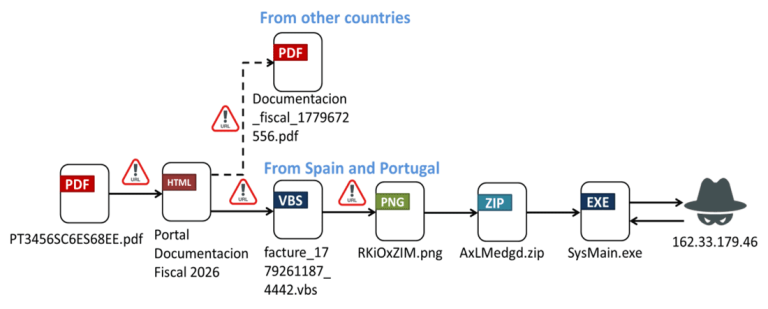
FortiGuard Labs discovered a new Ousaban banking trojan campaign. The attackers use geo-blocking to target banking users in Spain and Portugal.

FortiGuard Labs uncovered AsyncRAT AI lures using fake AI guides and an AutoHotkey loader to inject a stealthy .NET RAT into memory.

Read the latest Gafgyt malware analysis revealing how the dangerous COXMO botnet variant spreads via standalone scripts.

FortiGuard Labs exposes a highly evasive PureLogs info stealer campaign utilizing process hollowing and fileless execution.
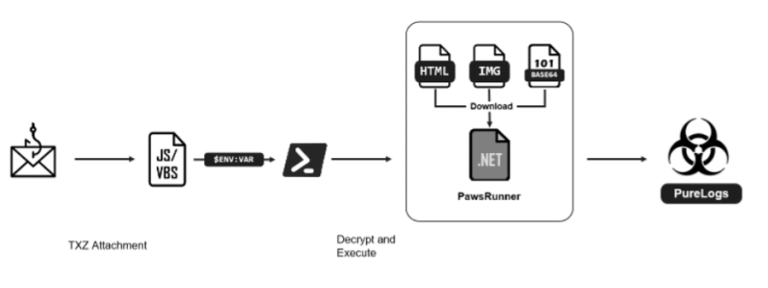
FortiGuard Labs warns of PawsRunner, a new .NET steganography loader hiding PureLogs infostealer payloads inside cat images to bypass corporate EDR.
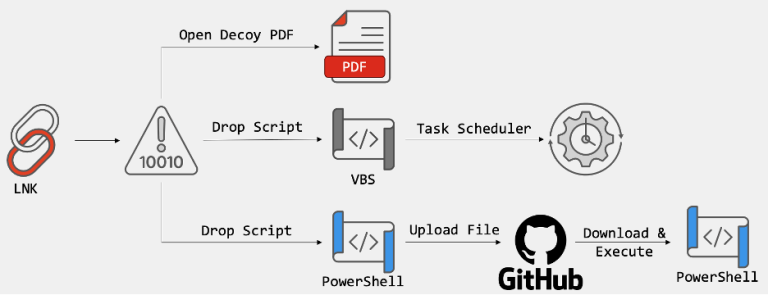
FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.
FortiGuard Labs exposes a massive Silver Fox APT campaign targeting Taiwan. Hackers use tax-themed phishing and BYOVD attacks to deploy Winos 4.0 malware.

Phishing emails use malicious Excel files to deploy XWorm RAT. The fileless attack exploits CVE-2018-0802 to steal data & control systems.

Interlock ransomware exploits a zero-day in gaming anti-cheat drivers to blind defenses. "Hotta Killer" tool targets education sector. Read the analysis.

INJ3CTOR3 hackers target FreePBX with EncystPHP web shell via CVE-2025-64328. Malware uses cron jobs for persistence. Patch immediately.

Attackers abuse GitHub, Dropbox, and the "Defendnot" research tool to disable Windows Defender and deploy Amnesia RAT & ransomware in Russia.

New fileless Remcos RAT campaign uses a "[virus detected]" shipping lure to inject malware into memory via process hollowing. See how to spot it.

A new report reveals a malware campaign using SEO poisoning to target Chinese-speaking users. Attackers use fake software sites to deliver Hiddengh0st and Winos.

A new phishing campaign is spreading MostereRAT, a sophisticated RAT that uses a Chinese scripting language and advanced evasion to bypass antivirus and EDR solutions.

A new report reveals the return of Gayfemboy, a Mirai-based IoT malware strain. It now uses advanced evasion techniques and targets multiple vendors to launch attacks.
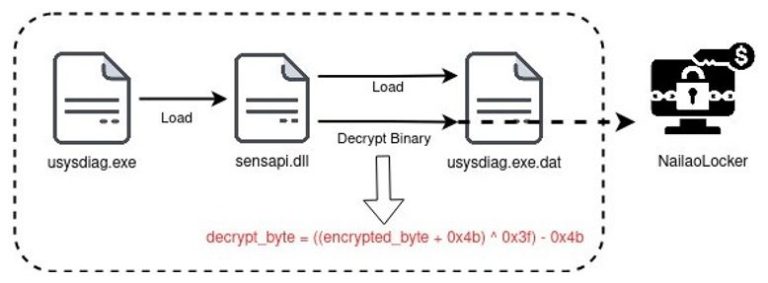
FortiGuard Labs unveils NailaoLocker, a new ransomware using Chinese SM2 encryption and a built-in, non-functional decryptor, suggesting a prototype or decoy.

FortiGuard Labs exposes NordDragonScan, a new infostealer using weaponized HTA scripts in Ukrainian-themed phishing. It performs recon, steals browser profiles, and exfiltrates documents.