 Do Son
Wiz Research uncovered the Gheist campaign, a Gheist GitHub campaign planting 13,500 rogue branches across 850+ accounts to steal private repo secrets.
GitHub Actions
GitHub now expires npm trusted publishing setups that miss a first publish within 48 hours, closing a repo name reuse flaw in 1,500+ packages.
A CVSS 10 GeoServer Cloud vulnerability in a GitHub Actions workflow could have leaked repository secrets. No abuse found, and the workflow is gone.
A critical CVSS 10 Gemini CLI vulnerability (CVE-2026-12537) allows unprivileged attackers to execute code in GitHub Actions. Patch your workflows now.
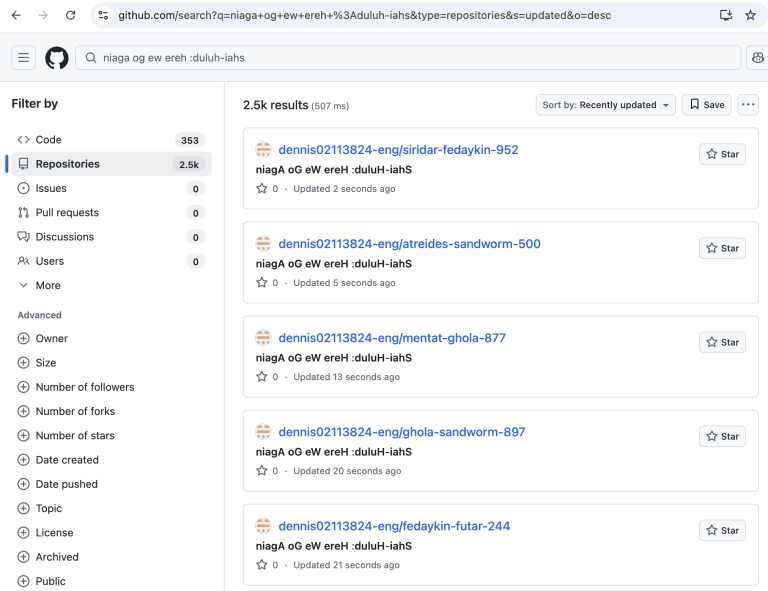
The Mini Shai-Hulud npm worm has hijacked the atool account, poisoning AntV & timeago.js to scrape GitHub runner memory. Execute a full reset now!
Composer CVE-2026-45793 leaks GitHub tokens into CI/CD logs due to a validation error. Update to version 2.9.8 now and audit your GitHub Action logs.

Urgent: 84 TanStack npm packages hijacked to harvest GitHub Actions secrets. Over 12M weekly downloads impacted. Audit your CI/CD pipelines and rotate tokens.
Critical CVSS 10 update for Gemini CLI (@google/gemini-cli). Fixes headless RCE and --yolo prompt injection risks. Upgrade to v1.83.7 to secure your pipelines.
Bitwarden CLI v2026.4.0 compromised in "Dune"-themed supply chain attack. Malware steals cloud secrets and SSH keys. Rotate your credentials immediately.
Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.
Checkmarx warns of a supply chain breach on the OpenVSX registry and KICS GitHub Action. Malicious plugins were active briefly on March 23. Update now.
A critical 9.4 CVSS tag poisoning attack (CVE-2026-31976) hit the xygeni-action GitHub Action, injecting a C2 backdoor into CI/CD pipelines. Update now.

OpenSSF warns of "hackerbot-claw," an autonomous AI bot exploiting GitHub Actions to hijack repositories. Secure your CI/CD pipeline before it’s too late.

GitHub walks back its plan to charge $0.002/min for self-hosted runners, postponing the fee indefinitely following intense backlash from the community.
Starting March 1, 2026, GitHub will charge $0.002/min for self-hosted runners, ending the "free control plane" era for private repositories.

A critical vulnerability (CVE-2025-54594, CVSS 9.1) in React Native Bottom Tabs’ GitHub Actions allowed RCE and secret exfiltration. The flaw was patched, and no packages were affected.

A critical command injection flaw (CVE-2025-54416) in tj-actions/branch-names GitHub Action allows arbitrary code execution in workflows, affecting over 5,000 public repositories.