 Do Son
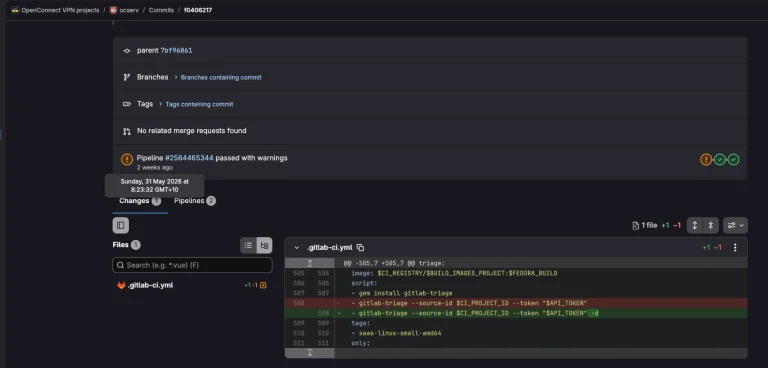
A critical GnuTLS token leak via a GitLab CI artifact exposure put major Linux distributions at risk. Learn how this supply chain vulnerability occurred.
GnuTLS
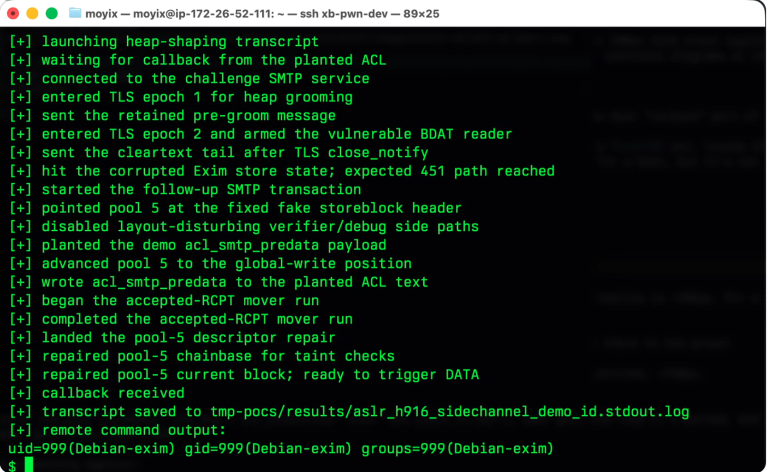
Urgent: Exim fixes a 9.8 severity RCE (CVE-2026-45185) affecting GnuTLS builds. A single-byte heap corruption allows for server takeover. Update to 4.99.3 now!

GnuTLS v3.8.13 fixes critical heap overwrites, identity truncation, and OCSP bypasses. Secure your Linux comms and upgrade to the latest version now.
GnuTLS v3.8.12 fixes high-severity DoS flaws (CVE-2026-1584). Malicious TLS 1.3 handshakes can crash servers. Update now to prevent outages.