
 Do Son
A critical 9.1 CVSS flaw in a Go auth library causes a Patreon "identity collision," merging all users into one account. Upgrade to v2.1.2 immediately!
Golang
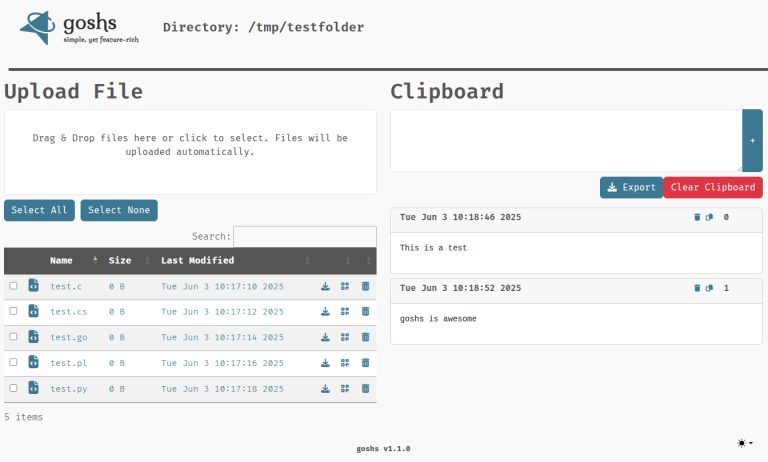
Critical 9.8 flaws in goshs v2.0.0-beta.2 allow unauthenticated attackers to write or delete any file on your system. Update to v2.0.0-beta.3 immediately!
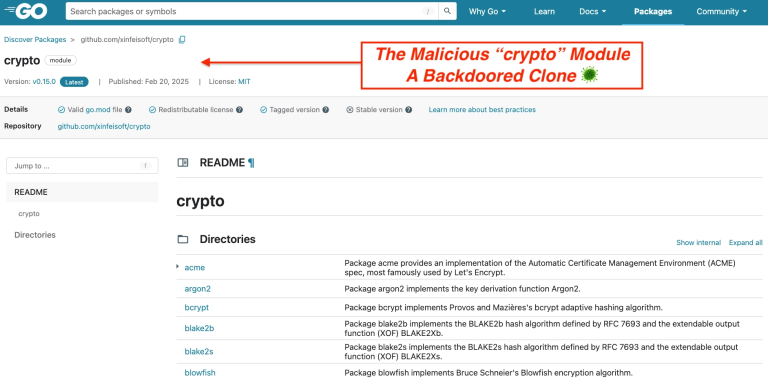
Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.

Critical Fiber framework vulnerability CVE-2025-66630 (CVSS 9.2) causes silent UUID failures, leading to session hijacking. Update to v2.52.11 now.
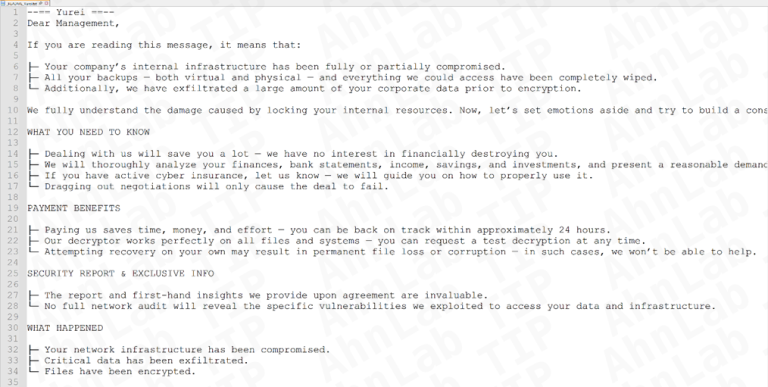
ASEC exposed Yurei, a new Go-based ransomware group using ChaCha20-Poly1305/ECIES for irreversible encryption. The stealthy RaaS operates with minimal initial setup and focuses on double extortion.

ASEC exposed Cephalus, a Go-based RaaS group attacking RDP. The malware uses VirtualLock, XOR encryption, and a fake AES key pattern to severely complicate memory and forensic analysis.

CYFIRMA uncovered Yurei Ransomware, a sophisticated Go-based double-extortion threat that uses ChaCha20 encryption, anti-forensic wipes, and disguises itself as WindowsUpdate.exe to propagate over SMB.

A critical flaw in LangChainGo, a popular LLM framework, allows attackers to read sensitive files via server-side template injection. A patch has been released.

Dire Wolf, a new Golang ransomware, is targeting manufacturing/tech in 11 countries. It uses double extortion, deletes backups, and has a "wipe mode" that permanently destroys files.

Go 1.24.4 and 1.23.10 fix flaws in net/http, os, and crypto/x509, addressing data leaks, file inconsistencies, and certificate validation bypasses. Update now!