 Do Son
Unit 42 exposes the new Gremlin stealer. It uses memory-resident techniques to hijack active browser session tokens and completely bypass MFA.
Gremlin Stealer
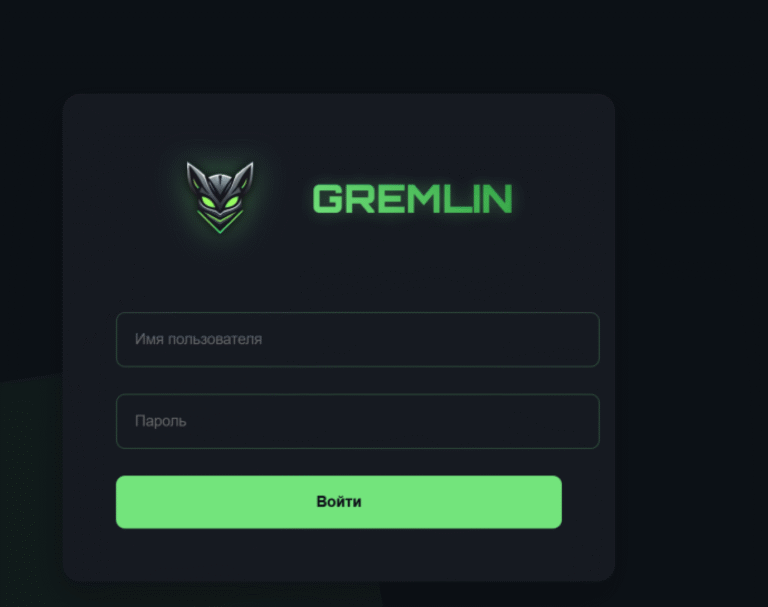
Gremlin Stealer malware, written in C#, exfiltrates browser data, crypto wallets, and VPN credentials, distributing stolen data via a Telegram-based backend.