 Do Son
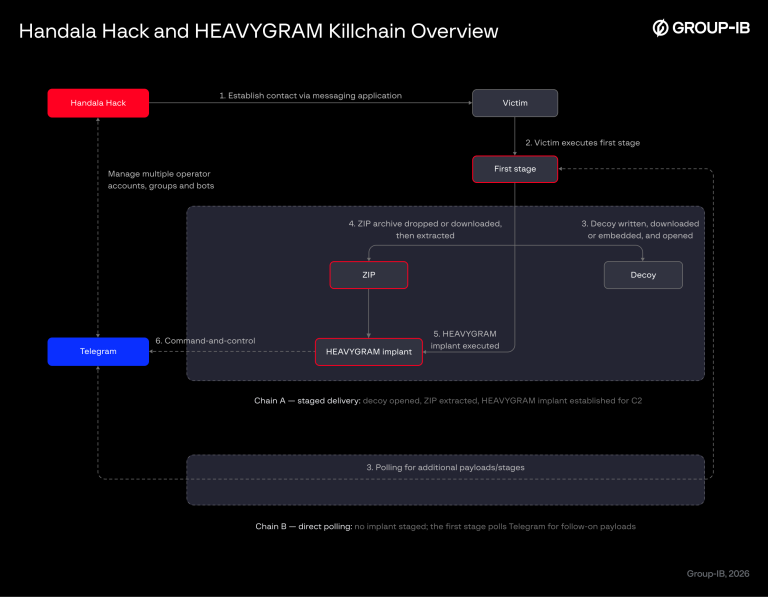
Group-IB uncovered Iranian HEAVYGRAM malware campaigns. The HEAVYGRAM malware abuses Telegram channels for command execution and data theft.
Handala Hack

The US DOJ has seized four domains used by Iran's MOIS to orchestrate global cyberwarfare, doxing, and death threats against dissidents and governments.
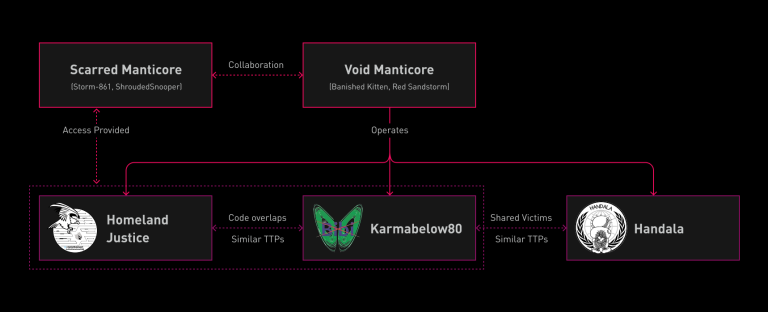
Check Point Research unmasks Handala Hack (Void Manticore), an Iranian MOIS threat actor using AI scripts and NetBird for destructive wiping attacks.