 Do Son
Discover how Microsoft is strengthening KMS activation by introducing hardware-based trust and TPM verification to combat forged licensing servers.
Hardware Security
Critical 9.2 CVSS flaw in WattBox 800/820 controllers (CVE-2026-41446) allows root RCE using plaintext hardware labels. Upgrade to firmware v2.10.0.0 now.
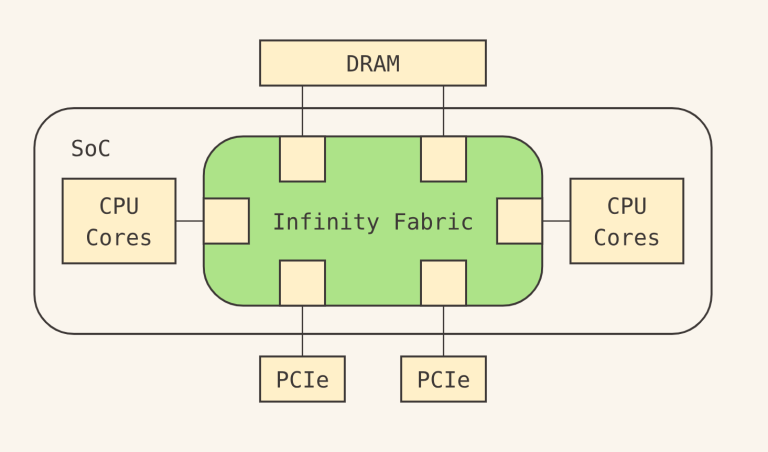
ETH Zurich researchers unmasked "Fabricked" (CVE-2025-54510), a flaw in AMD Infinity Fabric that bypasses SEV-SNP memory isolation. Patch your firmware today!
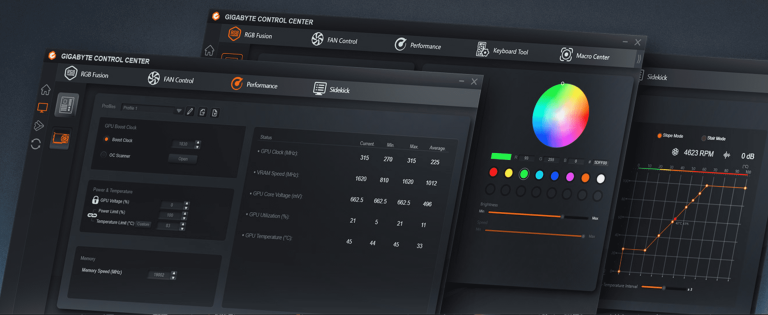
Gigabyte Control Center faces a critical 9.2 severity flaw (CVE-2026-4415). Unauthenticated attackers can write files and execute code—update to 25.12.10.01 now.
Eclypsium researchers reveal how compromised IP-KVM switches bypass EDR and software security to grant attackers total, BIOS-level system takeover.
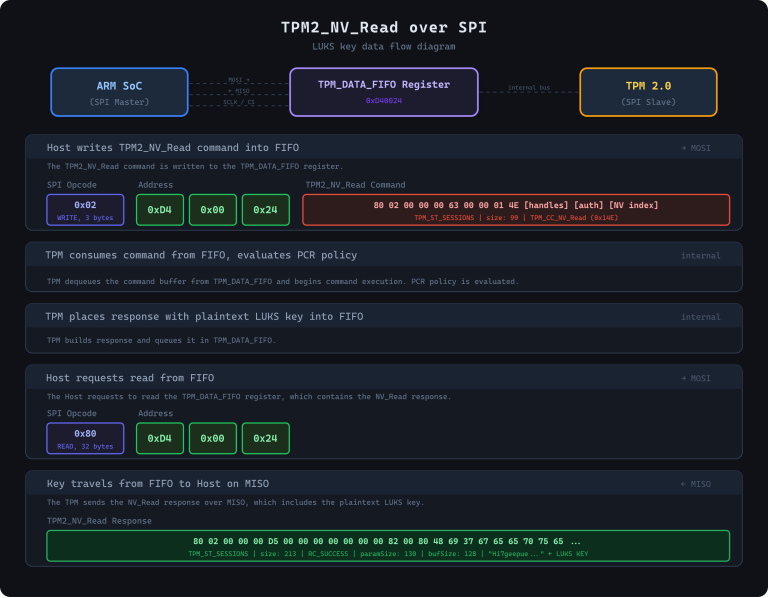
Researchers extract LUKS decryption keys in plaintext from Moxa UC-1222A devices via a novel TPM bus sniffing attack (CVE-2026-0714). Secure your hardware.

Microsoft begins rotating Secure Boot certificates in Jan 2026. Act now to prevent boot failures and maintain security before the June 2026 expiration.

GPUHammer is the first Rowhammer attack on GDDR6 memory (NVIDIA A6000), successfully inducing bit flips that can degrade AI model accuracy. Enable System-Level ECC to mitigate.

A TPM 2.0 flaw (CVE-2025-2884) allows local attackers to access sensitive memory or cause DoS. Update TPM firmware to protect trusted computing.