 Do Son
Patch two critical INFINITT PACS vulnerabilities today. Learn how CVE-2026-16305 and CVE-2026-16306 expose medical systems and secure your network now.
healthcare security
Quest Diagnostics data breach: hackers accessed patient records in its Quanum Lab Services Manager. Quest says it is not tied to the PHP flaw.

Threat actors are using RAR archive phishing to deploy Thailand healthcare malware. The campaign targets hospitals to steal credentials and sensitive data.
Orthanc v1.12.11 patches 9 critical flaws, including RCE risks and "decompression bombs" in DICOM servers. Secure your healthcare data—upgrade now!

Trend Micro uncovers a selective PureLog Stealer campaign using fake legal notices and fileless execution to target healthcare and government sectors.

A joint advisory warns of INC Ransom's devastating pivot to the Pacific. Discover how this RaaS group uses double extortion to target healthcare sectors.
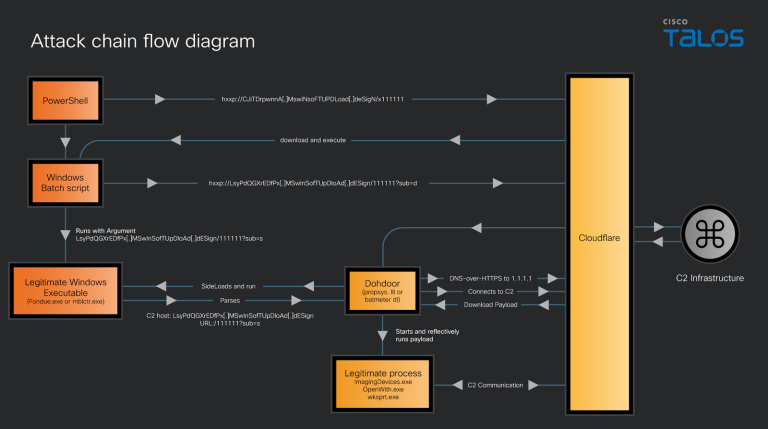
Cisco Talos uncovers "Dohdoor," a stealthy backdoor used by UAT-10027. It abuses DNS-over-HTTPS via Cloudflare to spy on U.S. healthcare and education sectors.

New CrazyHunter ransomware targets healthcare with BYOVD tactics and rapid encryption. Trellix reveals how this "greedy" threat cripples hospitals.

Jolly Scorpius has upgraded its Mario ransomware with multi-layered, dual-key encryption and dynamic chunking to bypass recovery and lock down data.

A high-severity vulnerability (CVE-2025-1701) in MIM Admin service allows local code execution with elevated privileges, impacting medical imaging environments.