 Do Son
SilabRAT malware, aka SnappyClient, is a $5K/month MaaS RAT flagged as HijackLoader. It uses HVNC and cracks crypto wallets, per Group-IB.
HijackLoader
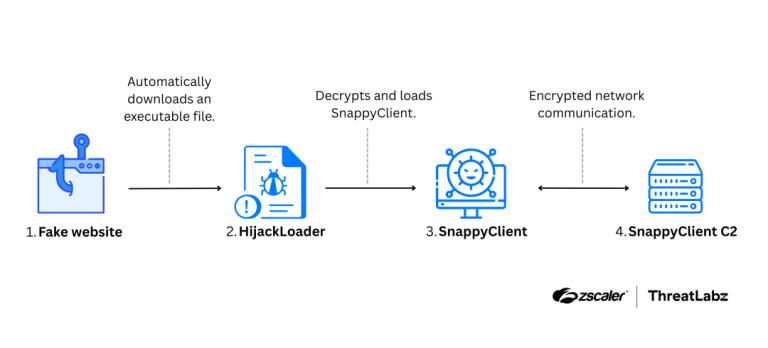
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.

G DATA reveals how pirated gaming site PiviGames distributes ACRStealer via "spaghetti code" HijackLoader and DLL sideloading, causing total account takeovers.

Attackers exploit GitHub forks ("Repo Squatting") to push HijackLoader malware via official-looking URLs. Technique remains active; verify all downloads.

A new report reveals HijackLoader, a Malware-as-a-Service loader. It uses advanced evasion and anti-analysis techniques to deliver stealers and other payloads.

A new report reveals a dangerous malware campaign on a popular game piracy site, proving that even with an adblocker, pirated software is a huge risk.
Splunk exposes a campaign weaponizing Inno Setup installers to deploy RedLine Stealer, using obfuscated Pascal scripts and HijackLoader to steal browser/crypto data.

HijackLoader and DeerStealer are surging, using ClickFix social engineering and sophisticated evasion to bypass defenses and exfiltrate sensitive data.

Explore the latest updates on HijackLoader malware and its stealthy modules designed to evade detection and expand capabilities.

Learn about Emmenhtal, a stealthy malware loader that employs LOLBAS tactics to deliver undetected malware strains like Lumma and Amadey.

Beware of the new cybersecurity threat, ClickFix. Discover how cybercriminals are leveraging this dangerous tactic to deceive users and distribute malware.