 Do Son
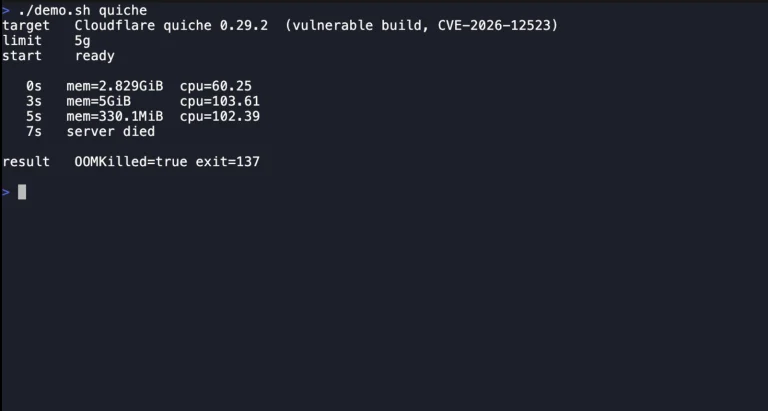
FoxIO released details and PoC code for a QPACK amplification attack that can crash HTTP/3 servers, including quic-go, quiche, lsquic and Bun.
HTTP/3
A public PoC now details CVE-2026-42530, an NGINX HTTP/3 RCE from a QPACK use-after-free. Upgrade to NGINX 1.31.2 to close the flaw now.

Two critical NGINX vulnerabilities, CVE-2026-42530 and CVE-2026-42055, let remote attackers crash workers and possibly run code. Patch NGINX now.

NGINX 1.30.1 fixes a 9.2 CVSS RCE flaw (CVE-2026-42945) and five other critical vulnerabilities. Protect your web infrastructure and update immediately!