
 Do Son
A critical 9.1 CVSS flaw in Spring Security (CVE-2026-22732) fails to write HTTP headers, exposing Java apps to severe data leaks. Update immediately.
HTTP Headers
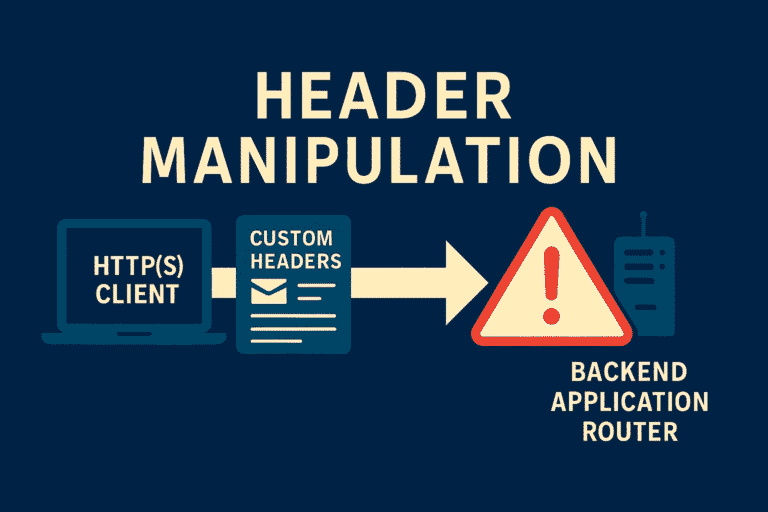
A critical flaw in Fabio load balancer allows malicious clients to manipulate or strip HTTP headers, leading to potential access control bypass. Upgrade to 1.6.6.
HTTP headers are widely used during web scraping because they allow access to otherwise blocked information. Competitor...