 Do Son
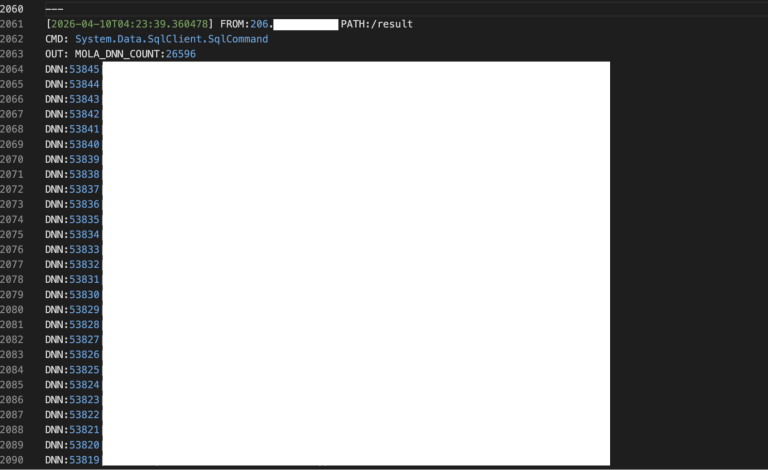
Hunt Intelligence uncovers a massive Iranian-nexus breach targeting the Omani Ministry of Justice. 26k records leaked via an unprotected UAE staging server.
Hunt Intelligence
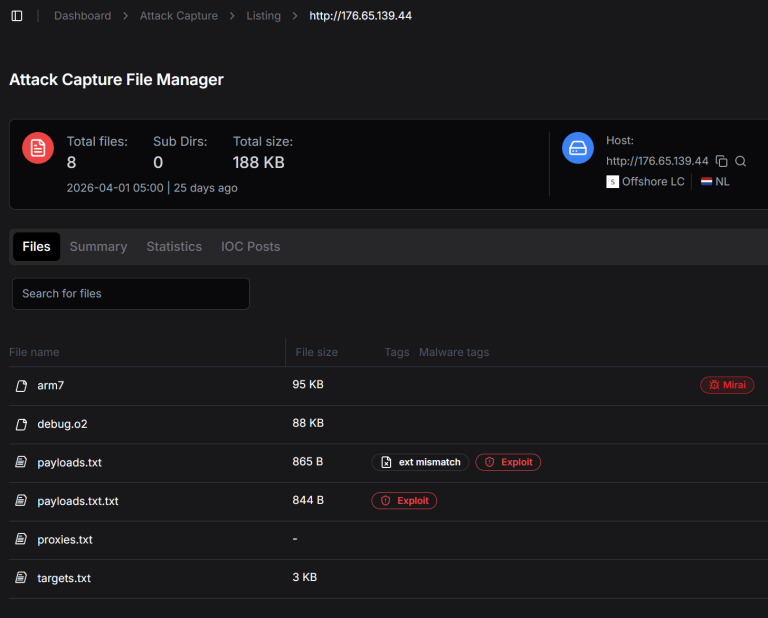
Hunt Intelligence dismantles xlabs_v1, a Mirai-derived botnet targeting 4M Android devices via port 5555. See how an exposed server leaked the entire toolkit.

Hunt Intelligence uncovers the "Hex" botnet, a stealthy campaign using stolen SSH credentials and on-host compilation to evade traditional binary scanners.
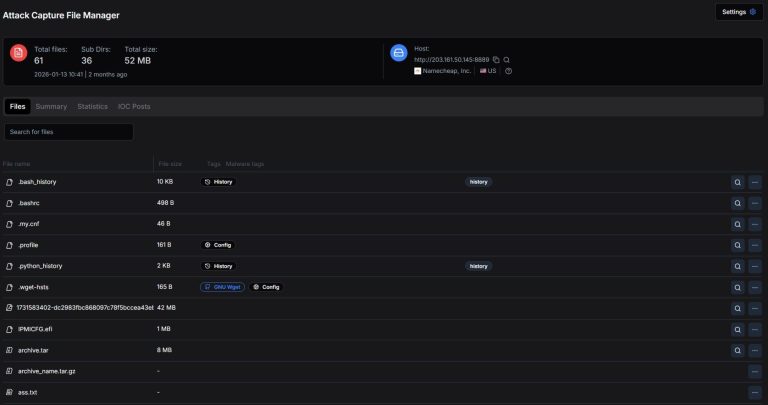
Hunt Intelligence unmasks APT28's 'Roundish' toolkit from an exposed server, revealing advanced CSS side-channel attacks and stealthy Linux implants.

A new report reveals attackers are abusing ScreenConnect to deliver AsyncRAT and custom malware payloads, a serious supply chain risk for enterprises and MSPs.