 Do Son
Group-IB analyzes over 280 samples of SiriusQT RAT. Discover how the Windows SiriusQT RAT uses HVNC, six persistence methods, and 100+ stealer targets.
HVNC
Varonis Threat Labs analyzed Dolphin X stealer, a forum-sold RAT with 300+ credential targets and an AI Profiler that ranks victims for operators.
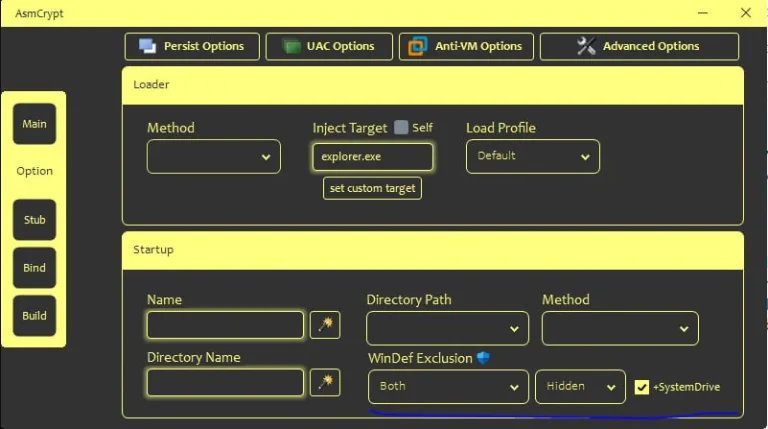
SilabRAT malware, aka SnappyClient, is a $5K/month MaaS RAT flagged as HijackLoader. It uses HVNC and cracks crypto wallets, per Group-IB.
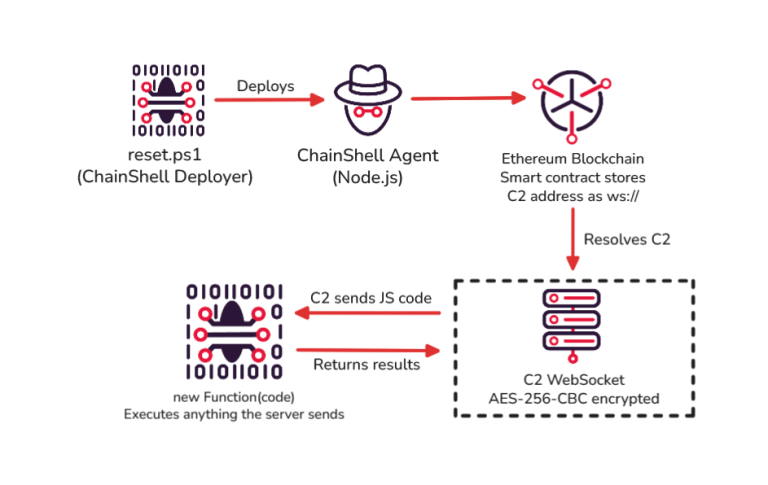
Iranian state actor Muddy Water adopts CastleRAT and ChainShell to hijack browsers and bypass MFA invisibly. A professional-grade shift in APT strategy.

eSentire TRU uncovers STX RAT, a modular Trojan targeting finance with HVNC, AMSI Ghosting, and advanced encryption. Secure your perimeter—learn how it works.

A unique Android banking trojan, FvncBot, targets mBank (Poland) customers. It uses HVNC and H.264 to stream screens and performs web-inject attacks via FCM/WebSocket C2.

Koi Security exposed GlassWorm, the first VSCode worm that spreads autonomously, using invisible Unicode to hide malicious code. It uses Solana blockchain and Google Calendar for a resilient C2.

CYFIRMA uncovers EdskManager RAT, a sophisticated remote access trojan using HVNC, multi-stage execution, and advanced persistence for covert, long-term system access.