 Do Son
A Keycloak account takeover flaw, CVE-2026-18963, lets attackers reset any user's password with no email verification. Update to 26.7.2 now.
Identity and Access Management
CERT/CC discloses six Logto vulnerabilities, including CVE-2026-15611 and CVE-2026-15616, that enable SSO authentication bypass and MFA skipping.

A critical 9.3 CVSS XSS vulnerability (CVE-2026-29191) in ZITADEL's SAML endpoint allows unauthenticated 1-click account takeover. Upgrade immediately.
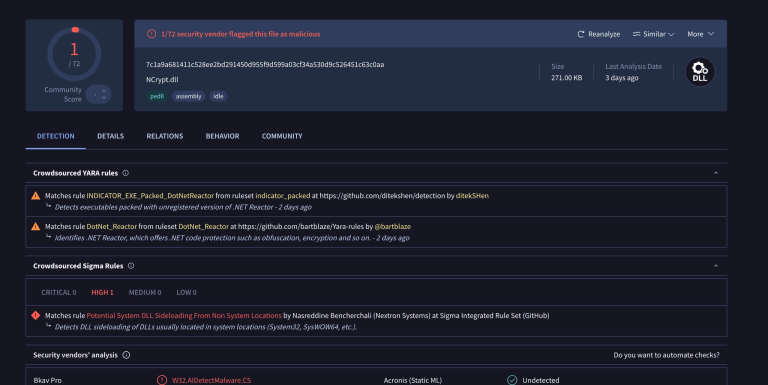
Socket researchers uncover a NuGet supply chain attack using "NCryptYo" to hijack ASP.NET apps. Attackers inject backdoors into production authorization layers.
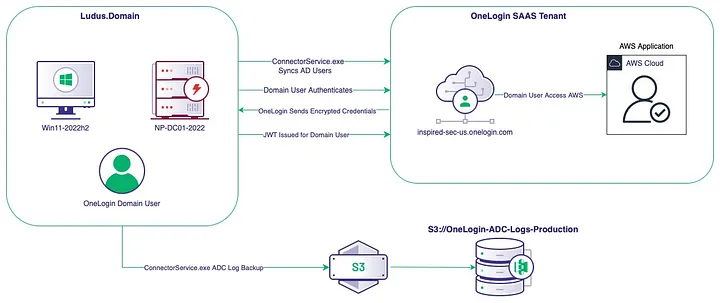
A critical flaw in OneLogin's AD Connector exposed API keys, allowing attackers to impersonate users across organizations via unclaimed S3 buckets and forged JWT tokens.