 Do Son
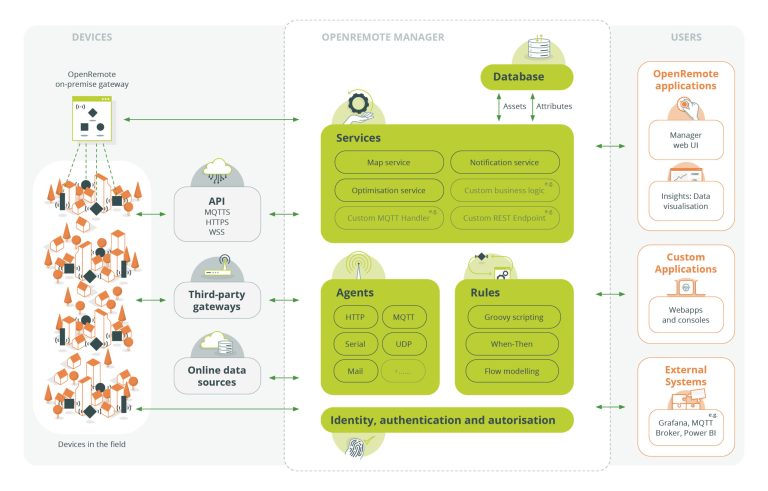
An OpenRemote vulnerability, CVE-2026-66013 (CVSS 9.3), enables unauthenticated asset takeover. Full advisory details are now public. Patch to 1.26.2.
IDOR

SolarWinds patched 15 critical Serv-U vulnerabilities enabling privilege escalation, account takeover, and RCE as root. Update to Serv-U 2026.3 now.
Four critical Coolify vulnerabilities let low-privileged users reach remote code execution and cross-tenant server access. Update to v4.1.2 now.
A critical 9.9 CVSS IDOR flaw in Comet Backup allows complete cross-tenant account takeovers. Self-hosted administrators must patch servers immediately!
Critical vulnerabilities in Vaultwarden (like CVE-2026-27898) allow privilege escalation and unauthorized access to secrets. Update to version 1.35.4 now.

TP-Link fixes critical IDOR (CVE-2025-9520) in Omada Controller allowing admins to hijack Owner accounts. Update now to prevent total network takeover.

A flaw in Apache Fineract risks Authorization Bypass via IDOR (CVE-2025-58137) in its self-service API, potentially exposing customer data. Also fixed: Weak Password Policy and Unmasked Server Keys. Update to v1.13.0.

Critical CVSS 9.9 RCE, IDOR, and path traversal flaws in InnoShop with full PoC exploit. No patch available—eCommerce sites at serious risk.