
 Do Son
Apple is reportedly manufacturing all four iPhone 17 models in India for the first time, marking a major shift in its strategy to reduce reliance on China.
India

OpenAI has launched a new low-cost "ChatGPT Go" subscription in India, a strategic move to convert users in a key market with cheaper pricing and extended features.
Phishing Scam Alert: McAfee Uncovers a New Android Campaign Impersonating a Government Solar Program

Phishing Scam Alert: McAfee Uncovers a New Android Campaign Impersonating a Government Solar Program
A new phishing campaign in India uses fake government solar subsidy websites to trick victims into downloading a malicious app that steals UPI PINs and other data.

CloudSEK warns of a surge in Raksha Bandhan-themed phishing, fake websites, and UPI scams in India. Attackers use courier lures, fake e-stores, and social engineering to steal money.
Apple commits an additional $100 billion to US industries, bringing its total investment to $600B. The move is a strategic response to new 25% tariffs on goods from India.

McAfee uncovers a new Android malware campaign targeting Indian users. The malware impersonates major banks to steal financial data and silently mines Monero in the background.
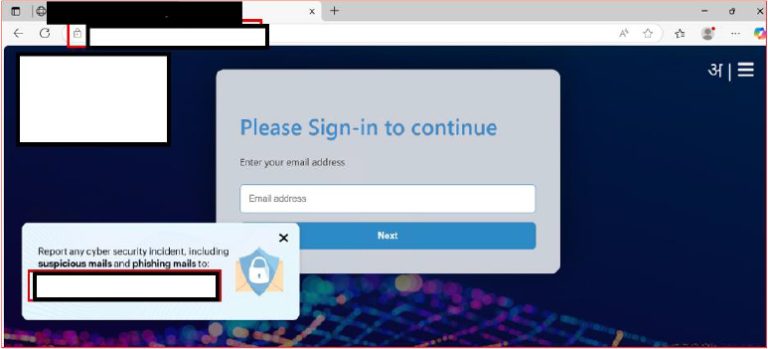
APT36, a Pakistan-linked threat actor, is targeting Indian government officials with phishing campaigns that mimic official websites to harvest credentials and Kavach MFA OTPs in real time.

A new report reveals APT36 (Transparent Tribe) is escalating cyber-espionage against India, using phishing and .desktop files to deploy the Poseidon backdoor for long-term access.

A CoinDCX software engineer, Rahul Agarwal, has been arrested in connection with a $44M crypto heist after an internal probe linked the breach to his compromised work laptop.

India aims to launch its first "Made in India" chip and open six fabs by late 2025 to boost domestic semiconductor manufacturing and reduce 90% import reliance.
APT36 (Transparent Tribe) is now targeting Indian government agencies via BOSS Linux with spear-phishing. It uses malicious .desktop files to deploy Go-based malware for espionage.

APT36 is targeting Indian defense personnel with sophisticated phishing, using fake NIC documents and multi-layered malware to steal sensitive data and evade analysis.

DRAT V2, a new Delphi-compiled RAT from TAG-140 (SideCopy/Transparent Tribe), is targeting Indian government entities with expanded post-exploitation and refined C2 techniques.

A new Android spyware campaign uses a "Wedding Invitation" APK via WhatsApp to install SpyMax RAT, stealing OTPs, contacts, and banking credentials from Indian users.

Proofpoint reveals TA397 (Bitter APT) is an India-aligned state-backed group conducting long-term espionage campaigns globally, targeting rivals and partners.

Amidst India-Pakistan tensions, Bitter APT launched a spear phishing campaign against Pakistan Telecommunication Company, using WmRAT for espionage.
A sophisticated phishing campaign, possibly by APT36, spoofs Indian government sites and uses ClickFix tactics to target Windows and Linux users.

The SideCopy APT group is evolving its tactics, using new methods like MSI packages and custom malware to target critical Indian sectors, including railways and oil & gas

Learn about India's new VPN policy and the implications for VPN users. Understand the requirements and potential risks involved.

Google Play Protect introduces enhanced fraud protection for Android users in India. Stay safe from malicious apps and cyber scams.
According to VentureBeat, Indian government officials announced today that the country will use artificial intelligence (AI) technology to...
According to NYTimes, India is seeking to establish a national identity system covering 1.3 billion people. It scans the...