
 Do Son
Operation ShadowRecruit targets Indian job seekers with SheetAgent RAT, abusing ControlR and Google Sheets for C2. Seqrite links it to APT36.
India

Mustang Panda targets India's government and hydropower sectors, abusing Zoho WorkDrive for C2. Acronis found new ZOHOMURK and MINIRECON implants.
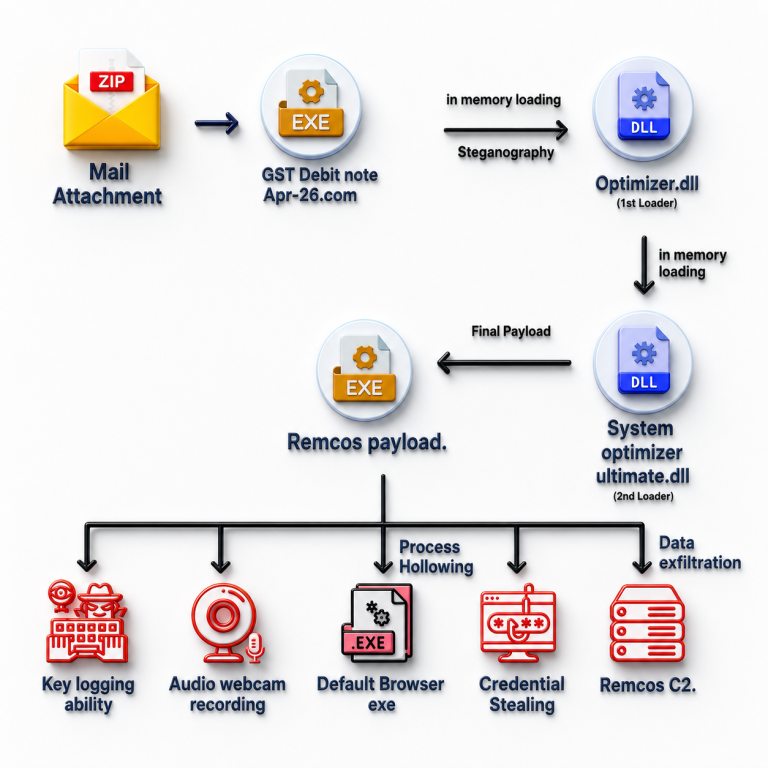
A steganographic loader hides Remcos RAT inside a bitmap and runs it in memory. K7 ties the fileless campaign to India via fake GST lures.
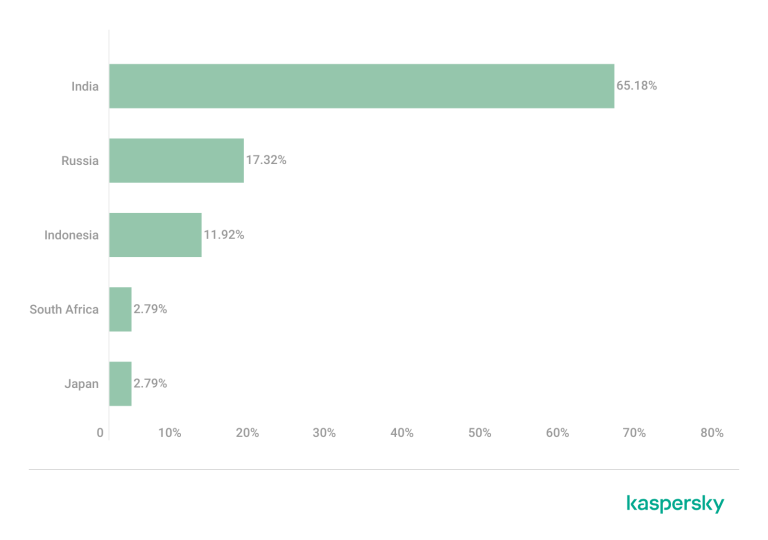
Silver Fox targets India and Russia with tax-themed phishing and the new ABCDoor backdoor. Learn how this Python-based threat hijacks screens and data.
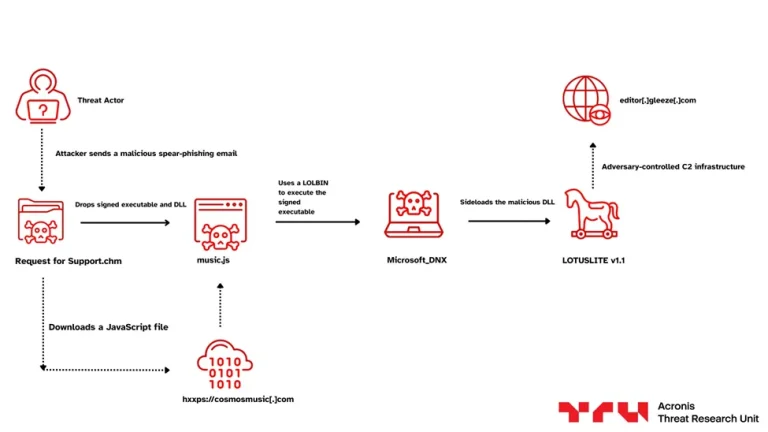
Mustang Panda targets India’s financial sector with the LOTUSLITE malware. Learn how this DLL sideloading campaign bypasses defenses for cyber-espionage.

India faces a revolt from Apple and Samsung over a 2026 proposal to mandate source code disclosure for security audits, sparking a major IP standoff.
CYFIRMA unmasks APT36's latest campaign: a fake JLPT exam lure using fileless LNK malware to evade antivirus and spy on Indian government targets.

Hyderabad police arrest another ex-Coinbase agent for selling user data. The TaskUs insider breach exposed 70k users and cost Coinbase up to $400 million.

CloudSEK’s TRIAD unmasks Silver Fox APT, a China-linked group using Valley RAT to target India while hiding behind misattributed tax phishing lures.

SEQRITE Labs uncovers a China-linked campaign targeting Indian firms with fake tax notices to install persistent Remote Access Trojans.

RTO Challan malware hijacks Android devices in India using a fake traffic ticket lure, a malicious VPN, and SMS interception to steal UPI PINs and Aadhaar data.

NexusRoute is a sophisticated Android RAT campaign impersonating Indian E-Challan/mParivahan via GitHub phishing. It steals UPI PINs and conducts surveillance using a native-backed and professionally maintained malware framework.

Makop ransomware operators now use GuLoader and BYOVD (ThrottleStop.sys) to bypass EDR and security. The "low-effort" campaign targets RDP-exposed networks, with 55% of attacks aimed at India.

India mandates the preinstallation of the Sanchar Saathi cybercrime app on all new smartphones. The app is non-removable, raising major privacy concerns for Android and Apple users.

Sekoia exposed TransparentTribe (Pakistan-linked APT) targeting Indian government with AI-assisted DeskRAT malware. The Golang RAT infects BOSS Linux via malicious .desktop files and staging servers.

A sophisticated GhostBat RAT campaign targets Indian users by spoofing RTO apps (mParivahan). The malware steals UPI credentials and OTPs via phishing pages and uses a Telegram bot for C2.

Apple's supply chain in India has created 350,000 jobs and grown to include 45 local partners. The entire iPhone 17 series is set to be fully assembled in India.

A new report reveals a surge in coordinated hacktivist attacks on India's critical infrastructure. Groups from Pakistan, Russia, and others are launching breaches and DDoS attacks.

A new AI scam network is targeting Indian social media users. It uses deepfakes of celebrities and fake news sites to promote fraudulent investment schemes.

A new report reveals how scammers are exploiting the Ganesh Chaturthi festival in India with fake websites, lottery fraud, and phishing to steal money and data.
A new report reveals that the Pakistan-linked APT36 is now targeting Indian government and defense entities with Linux-specific malware delivered via Google Drive.

A new report reveals that the Pakistan-based APT36 is targeting Indian government entities using spear-phishing and Linux-specific malware to steal sensitive data.