
 Do Son
New "Gopher Strike" & "Sheet Attack" campaigns hit Indian govt. Linked to Pakistan, attackers use GitHub C2 & GenAI malware to evade detection.
Indian government

CYFIRMA exposes APT-36 weaponizing a fake NCERT WhatsApp advisory to deliver a stealthy backdoor and seize long-term control of government systems.
Seqrite Labs uncovers APT36 phishing campaign using Pahalgam terror attack-themed lures to deploy Crimson RAT against Indian government targets.
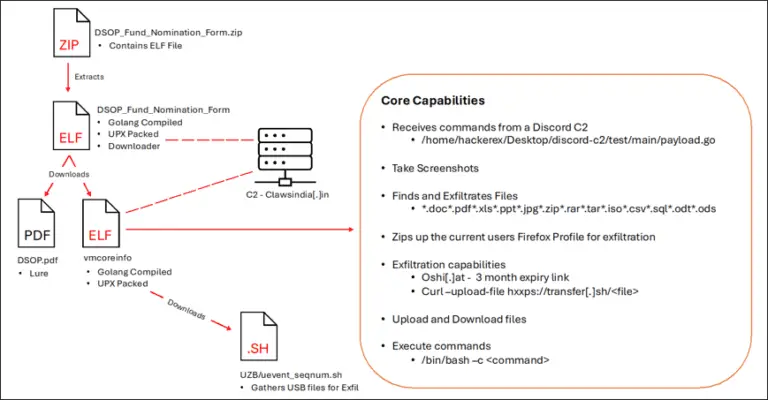
Researchers revealed a sustained campaign by Pakistani-based cyber espionage group APT36 targeting critical Indian government