 Do Son
JetBrains patched CVE-2026-75045, letting an unauthenticated attacker download YouTrack database backups. Eight flaws fixed. Update now.
Information Disclosure
TP-Link Kasa vulnerability CVE-2026-9770 (CVSS 8.6) lets local attackers intercept admin credentials on EC70 and EC71 cameras. Update firmware now.
QNAP QuMagie vulnerabilities let unauthenticated attackers access media files, causing information disclosure. Patch QuMagie and License Center now.
A critical Langflow file upload flaw (CVE-2026-55450) is public with a PoC, enabling unauthenticated denial-of-service and path disclosure. Patch 1.9.1.
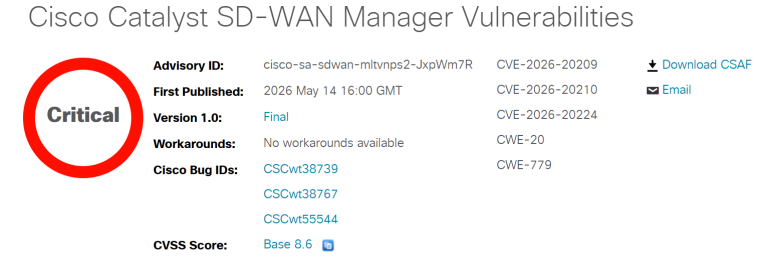
Cisco fixes a critical 8.6 CVSS XXE flaw (CVE-2026-20224) in Catalyst SD-WAN Manager. Unauthenticated attackers can read arbitrary files. Patch now!
Composer CVE-2026-45793 leaks GitHub tokens into CI/CD logs due to a validation error. Update to version 2.9.8 now and audit your GitHub Action logs.

Unpatched CVE-2026-5757 in Ollama allows unauthenticated heap memory exfiltration via crafted GGUF files. No patch available—secure your LLM servers now.

Cisco warns of active exploitation for CVE-2026-20133 in Catalyst SD-WAN Manager. Unauthenticated attackers can leak OS data. Patch by April 24, 2026.
Orthanc v1.12.11 patches 9 critical flaws, including RCE risks and "decompression bombs" in DICOM servers. Secure your healthcare data—upgrade now!

Squid Proxy patches critical 9.2 CVSS DoS and memory leak flaws in ICP. Standard access rules won't block the attack—upgrade to version 7.5 now.
Jenkins patches a high-severity stored XSS flaw (CVE-2026-27099) and an info disclosure bug. Update to version 2.551 or LTS 2.541.2 to secure pipelines.

CVE-2025-67732 unmasks a high-severity flaw in Dify that exposes plaintext API keys to frontend users. Upgrade to v1.11.0 to secure your AI quotas.

CVE-2025-68428 reveals a 9.2 critical flaw in jsPDF's Node.js build, allowing arbitrary file reads from servers. Upgrade to version 4.0.0 now!

Apache SIS patches a decade-old XXE flaw (CVE-2025-68280) that allows attackers to steal server files via malicious map data. Update to version 1.6!

Apache Kyuubi patches a high-severity 8.8 CVSS flaw (CVE-2025-66518) that allows unauthorized local file access via path traversal. Update to v1.10.3!

CISA adds MongoBleed (CVE-2025-14847) to its KEV Catalog after confirming active exploitation. 80,000+ MongoDB servers are at risk. Patch by Jan 19!

MongoBleed (CVE-2025-14847) allows unauthenticated MongoDB memory leaks. With Joe Desimone's PoC released, upgrade to v8.0.17 or v7.0.28 now!

LangChain patches a critical 9.3 CVSS flaw (CVE-2025-68664) where unescaped "lc" keys allow attackers to steal API secrets via prompt injection.

MongoDB CVE-2025-14847: A high-severity flaw in zlib compression allows unauthenticated attackers to read sensitive heap memory. Upgrade to v8.2.3+!

M-Files patches a high-severity flaw (CVE-2025-13008) that allows insiders to steal session tokens and impersonate users. Update to v25.12.15491.7!
A High-severity flaw (CVE-2025-63387) in Dify v1.9.1 allows unauthenticated users to access sensitive system configurations via an unprotected API.

Roundcube patches two High-severity flaws: an SVG-based XSS and a CSS sanitizer bypass. Protect your inbox—update to v1.6.12 or v1.5.12 now.