
 Do Son
Gootloader returns with malformed ZIPs to bypass detection. New alliance with Vanilla Tempest fuels Rhysida ransomware attacks. See the detection tips.
initial access

Rhysida ransomware is abusing Microsoft Trusted Signing to deploy OysterLoader (IAT) via Bing/Teams malvertising. The gang leveraged 40+ certificates to sign malware, bypassing security filters.

RVTools briefly hijacked in a Bumblebee malware supply chain attack. Learn how attackers used a trusted tool to deliver post-exploitation payloads.
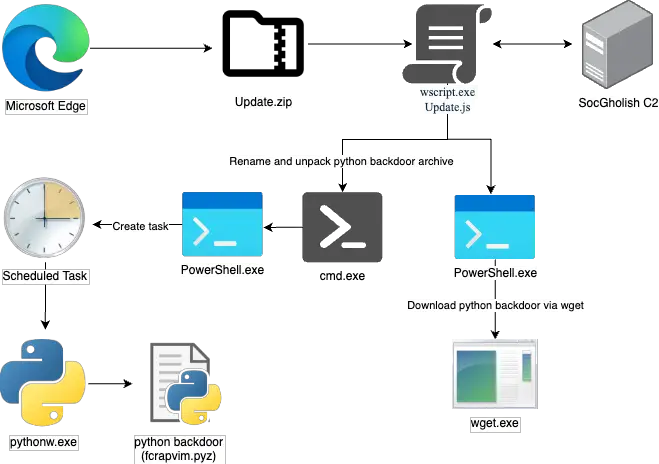
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.