 Do Son
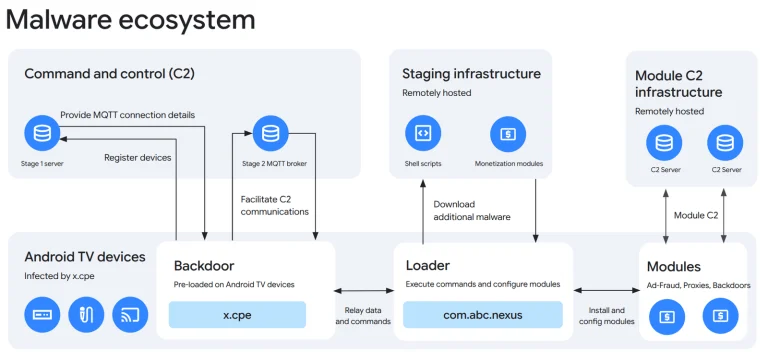
Google dismantled the Videostrong XCPE botnet infecting 1.3M set-top boxes. The XCPE botnet sold residential proxy access to cybercrime affiliates.
IoT botnet
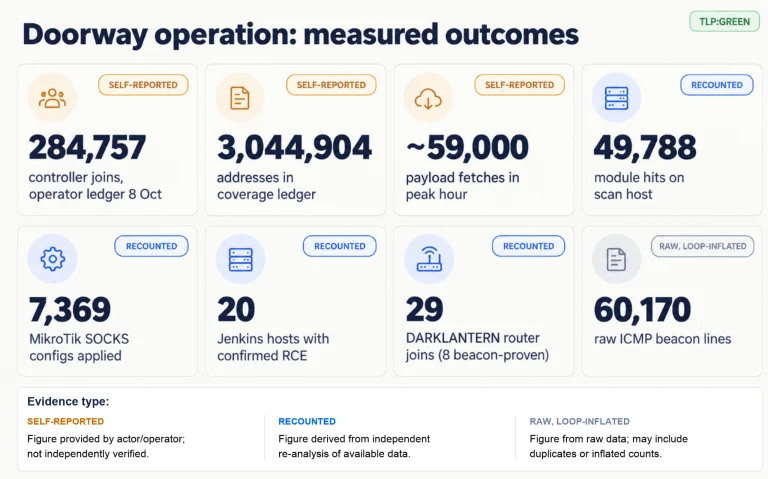
CloudSEK uncovers the Doorway botnet. The Rust Doorway botnet exploits routers, cameras, and servers to build a global proxy network.

The Dysphoria botnet uses blockchain ENS/SNS domains for covert C2 and turns victims into relays. XLab tracked over 200,000 bots in this IoT DDoS botnet.
Nozomi details the Tengu botnet, a modernized Mirai variant. This IoT malware adds encrypted C2, proxy, anti-analysis, and self-defense to resist removal.

Unit 42 exposed TuxBot v3 Evolution, an IoT botnet built with LLM help. AI-written bugs left the malware only 70% functional. See the full analysis.

Read the latest Gafgyt malware analysis revealing how the dangerous COXMO botnet variant spreads via standalone scripts.

A massive, long-running proxy botnet using outdated IoT devices for criminal anonymity has been dismantled in a global law enforcement operation.
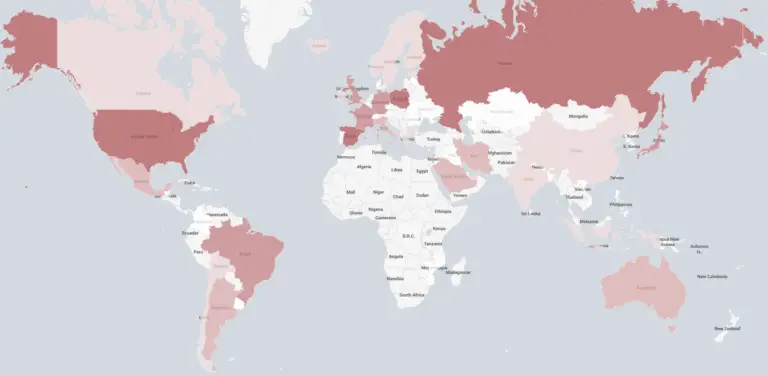
Discover how a newly discovered IoT botnet is targeting organizations globally with large-scale DDoS attacks.

CatDDoS-related gangs have leveraged a wide array of vulnerabilities across multiple vendor devices like Apache, Cisco, D-Link, Huawei, ...