 Do Son
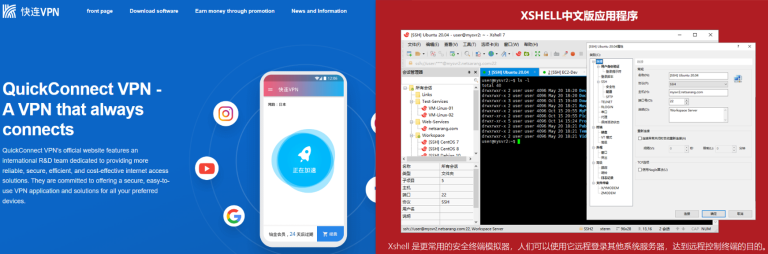
Kong RAT: A year-long SEO poisoning campaign targeting developers with trojanized SSH/VPN tools and .NET NativeAOT stealth. Learn how to stay protected.
IT security

Critical BeyondTrust flaw CVE-2026-1731 (CVSS 9.9) allows unauthenticated RCE on Remote Support & PRA appliances. Update to v25.3.2 immediately.
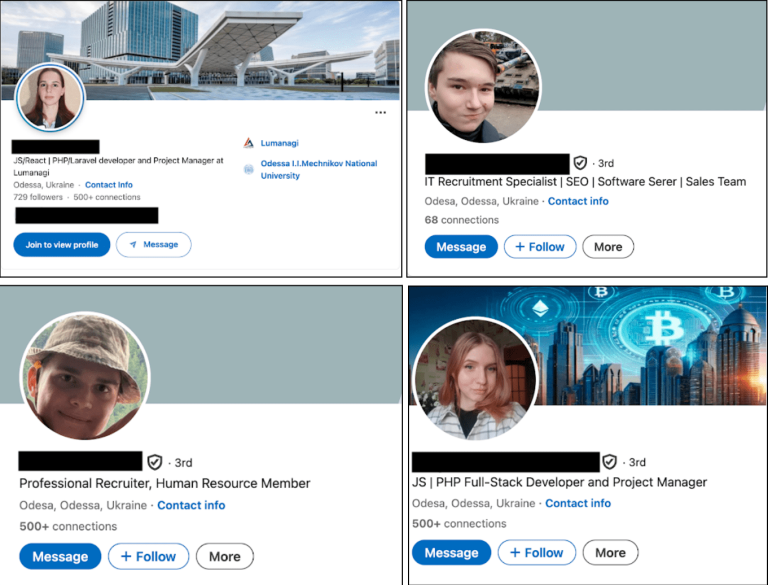
North Korean group PurpleBravo uses fake job offers to breach IT firms. The "Contagious Interview" campaign deploys malware via coding tests.

A new report reveals a persistent phishing campaign targeting ScreenConnect super admins. The stolen credentials are being sold to ransomware affiliates for future attacks.

Ex-Eaton programmer Davis Lu sentenced for planting a malicious “kill switch” that sabotaged company servers and caused massive financial losses.

Microsoft’s August Patch Tuesday fixes 119 flaws, including a publicly disclosed Kerberos zero-day (CVE-2025-53779) that could lead to domain admin privileges.

The Rainbow Hyena threat cluster is unleashing PhantomRemote, a new backdoor, in phishing attacks against Russia's healthcare and IT sectors, leveraging compromised emails.

B. Braun's OnlineSuite AP 3.0 faces severe vulnerabilities, including a CVSS 10.0 RCE, risking hospital IT and data. Immediate patching is crucial.