 Do Son
Ivanti security advisories fix 13 flaws, including Ivanti Endpoint Manager RCE CVE-2026-121653 (CVSS 9.8) and CSA bug CVE-2026-121683.
Ivanti EPMM
Ivanti released patches for high severity Ivanti vulnerabilities affecting Sentry and EPMM. Secure your enterprise deployments against these flaws now.

New Ivanti EPMM security updates address high-severity flaws that could allow a remote authenticated attacker to achieve remote code execution.
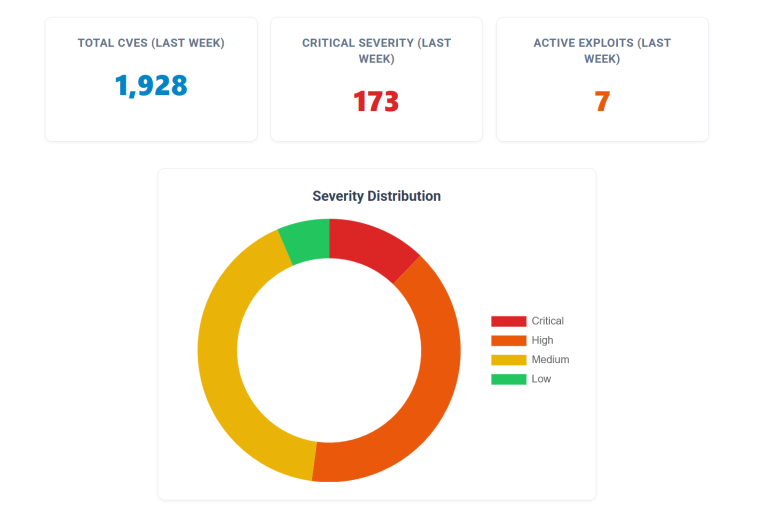
Weekly Security Digest: 1,928 new vulnerabilities hit the wire. From Palo Alto firewalls to LiteLLM AI gateways, here is how to prioritize your defense.

CISA adds critical Ivanti EPMM flaw (CVE-2026-1340) to KEV catalog. The 9.8 CVSS code injection allows unauthenticated RCE. Patch mandated by April 11!

Ivanti EPMM under attack via zero-days CVE-2026-1281 & 1340. Hackers use bash scripts to plant dormant backdoors. Patch immediately.

New campaign targets Ivanti EPMM with dormant in-memory backdoors. Attackers use CVE-2026-1281 to plant "sleeper" agents. Restart servers immediately.

Ivanti confirms critical EPMM RCE flaws (CVE-2026-1281) are exploited in the wild. Unauthenticated attackers can compromise MDM. Patch immediately.

A critical zero-day (CVE-2025-4428) in Ivanti EPMM is exploited by UNC5221, enabling unauthenticated RCE and data theft across multiple sectors.