 Do Son
PwnEscape (CVE-2026-99999) is a critical Linux kernel VM escape that let a guest run code as root on the host in lab tests. Update your kernel now.
KVM
A critical KVM guest escape (CVE-2026-89775) enables an LPE to gain root on Linux hosts. Patch this KVM guest escape vulnerability now.
CVE-2026-50112 is a critical Apache CloudStack flaw enabling cross-tenant remote code execution as root on KVM hosts. Upgrade to 4.20.3.1 or 4.22.1.1.

PoC exploit code is public for CVE-2026-64561 (Zapscape), a KVM escape that runs commands with kernel root privilege on the host. Details inside.
OVH patched CVE-2026-53359, a critical KVM flaw, across tens of thousands of hosts in under 10 days without warning most clients first.
Linux kernel CVEs surged to 440 advisories in just 24 hours, with many flaws found by AI. Most are already patched, so update your kernel promptly.
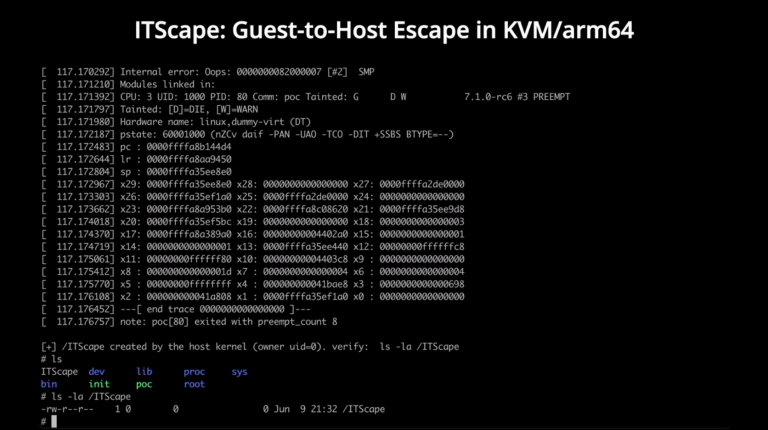
The ITScape KVM escape vulnerability (CVE-2026-46316) threatens arm64 clouds. Details and a guest-to-host escape exploit PoC are now publicly disclosed.

A critical Linux KVM flaw allows guests using Intel AMX to trigger host kernel panics. Fixes are underway for modern kernels (5.17+) to prevent host DoS.

A critical flaw (CVE-2025-52562, CVSS 10.0) in Convoy KVM panel allows unauthenticated remote code execution via directory traversal.