 Do Son
A critical LiteLLM vulnerability (CVSS 10.0) lets an unauthenticated file read leak the master key on Enterprise proxies. Update to 1.106.5 now.
LiteLLM
A LiteLLM supply chain attack shipped a PyPI credential stealer in version 1.107.0 that grabs cloud, AI tool, and SSH secrets. Act now.
Hackers exploit CVE-2026-35029 in the wild. Prevent a LiteLLM vulnerability server takeover and safeguard exposed secrets.
A critical LiteLLM authentication bypass (CVE-2026-49468) lets crafted Host Header Injection reach protected AI Gateway routes. Patch in 1.84.0.
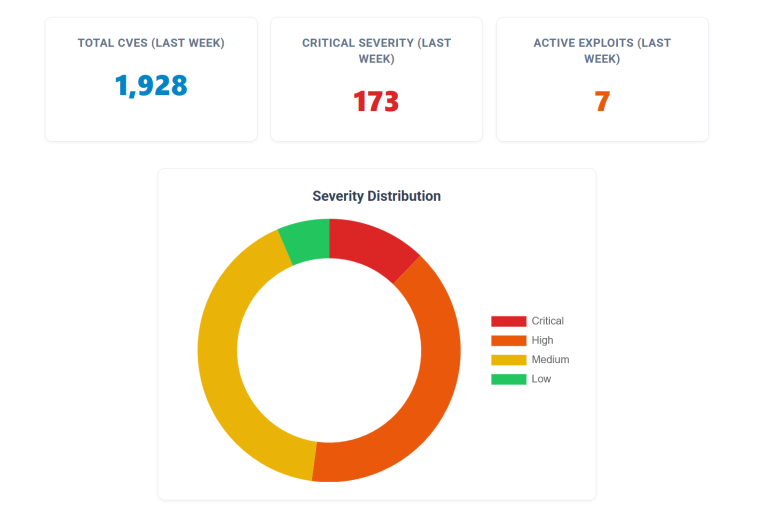
Weekly Security Digest: 1,928 new vulnerabilities hit the wire. From Palo Alto firewalls to LiteLLM AI gateways, here is how to prioritize your defense.
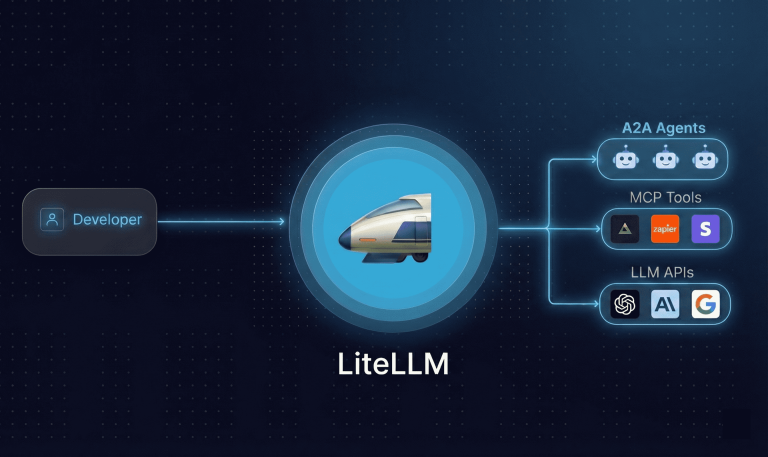
LiteLLM CVE-2026-42208 is under active exploitation. Attackers are using SQL injection to steal AI credentials. Patch to v1.83.7 and rotate keys immediately.
LiteLLM patches critical 9.4 CVSS flaws, including OIDC cache collisions and pass-the-hash attacks. Secure your AI infrastructure—upgrade to v1.83.0 now!
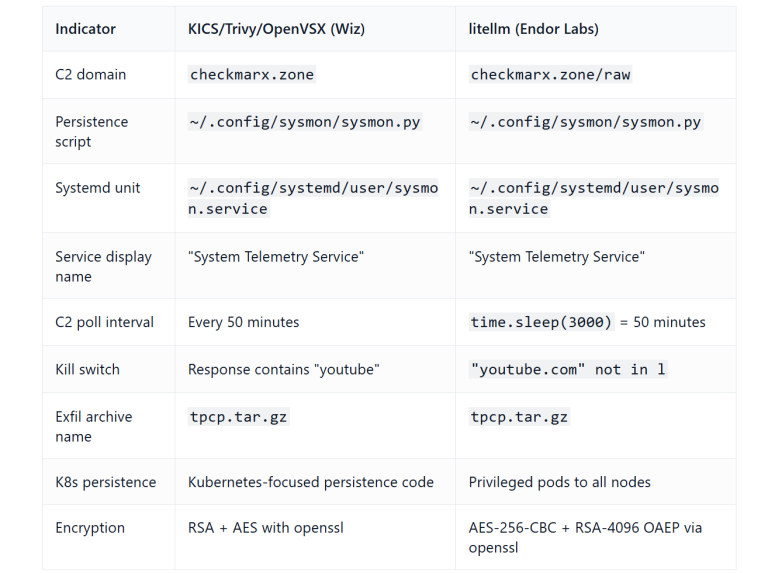
95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.