 Do Son
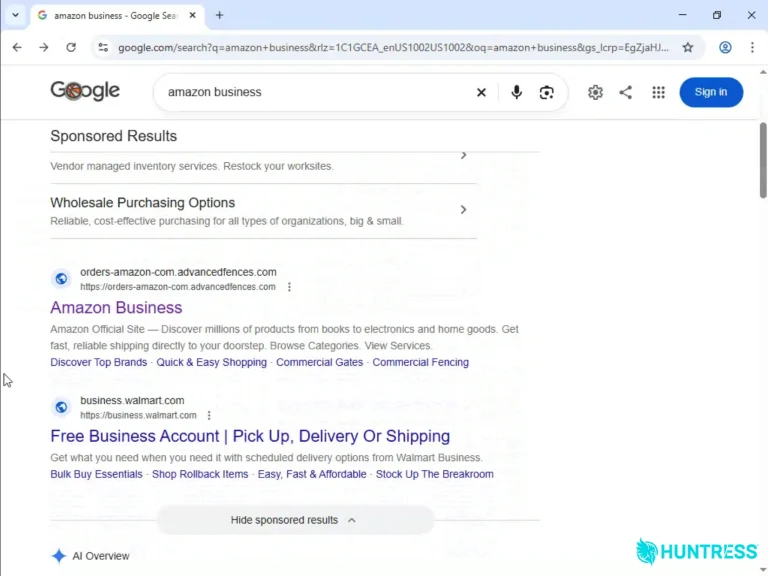
An Amazon ClickFix campaign uses a fake CAPTCHA and the old Windows finger command to drop Lumma Stealer and NetSupport. Stay protected.
LOLBIN

New Fake CAPTCHA campaign uses Google Calendar & steganography to drop Amatera Stealer. See how this attack exploits legitimate Windows tools to stay hidden.

Storm-0249 IAB abuses the SentinelOne EDR process via DLL sideloading to evade detection. The group uses LoLBin tools for fileless execution and sells access to ransomware groups like LockBit.

19 malicious VS Code extensions bypassed detection by hiding a Rust trojan in tampered node_modules and a fake banner.png using steganography. The attack uses cmstp.exe (LOLBIN) for execution.