 Do Son
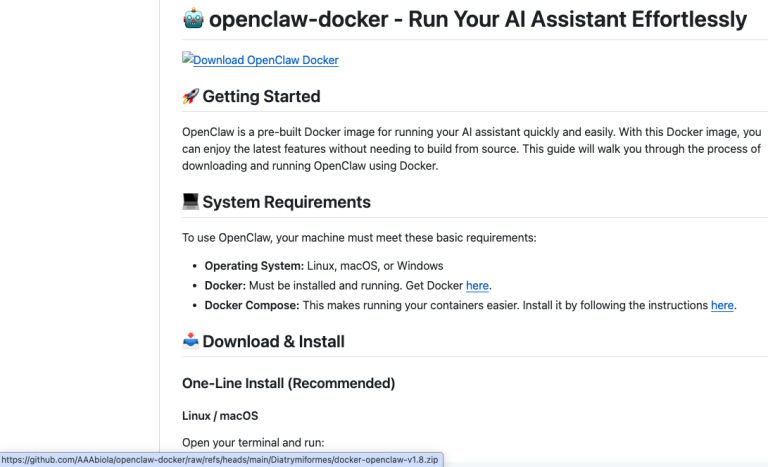
Netskope uncovers TroyDen’s Lure Factory, an AI-powered operation using 300+ trojanized GitHub repos and a 29,000-year sleep to steal credentials.
LummaStealer

LummaStealer is back, evading takedowns with "ClickFix" tactics. Bitdefender reveals how fake CAPTCHAs trick users into running malware. Stay alert.

LummaStealer evolves into a sophisticated Malware-as-a-Service, using stealth and advanced techniques to steal data.

Uncover the LummaStealer Attack and its new malvertising tactics using fake booking websites to distribute info-stealer malware.

Beware of cracked software and fake installers. Discover how cybercriminals exploit user trust and spread malicious payloads.
Discover HeartCrypt, the powerful Packer-as-a-Service used by cybercriminals to protect malware from detection.