 Do Son
New details on the Operation FlutterBridge malware reveal a sneaky WebView-based architecture designed to hijack Chrome browsers on macOS.
MacOS backdoor
Urgent: Malicious Nx Console v18.95.0 briefly hit the VS Code Marketplace, targeting 2M+ installs with a macOS backdoor and token stealer. Audit now!
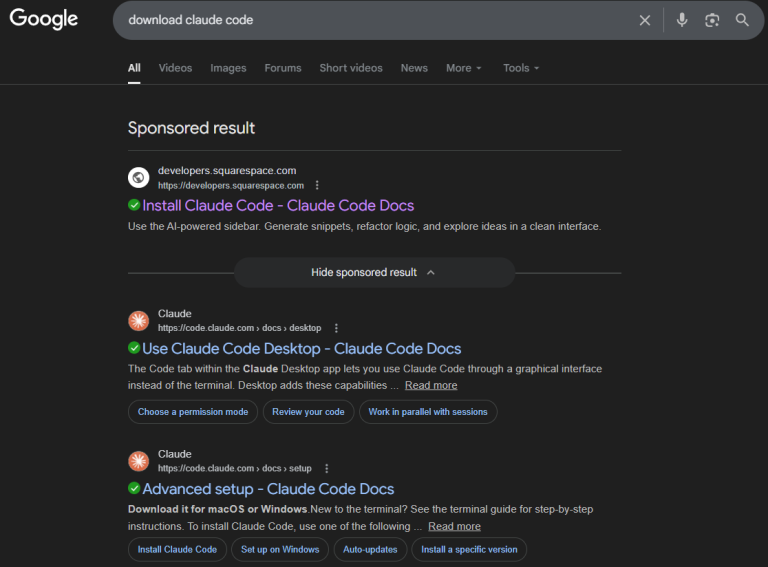
Bitdefender exposes a malvertising campaign targeting developers searching for Claude Code. Fake Google Ads deploy Windows stealers and macOS backdoors.

A new macOS backdoor, ChillyHell, bypassed Apple's notarization process for years, remaining undetected while being used for espionage and brute-force attacks.
Learn about the emergence of HZ Rat backdoor on macOS, targeting DingTalk and WeChat users. Stay vigilant against this new threat.

Bitdefender has uncovered a never-before-seen backdoor targeting Mac users, christened Trojan.MAC.RustDoor.

These repackaged applications, laced with a Trojan proxy and a post-install script, mark the first step in a meticulously planned infection process.