 Do Son
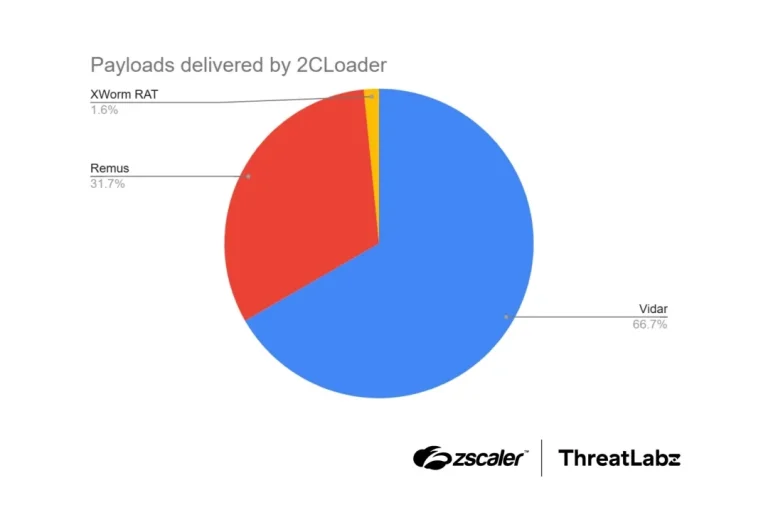
2CLoader malware dodges sandboxes and security tools to deliver Vidar and Remus infostealers. See how it works and how to detect it.
malware loader
CastleLoader malware now delivers NeedleStealer, a Rust crypto wallet spoofer and Golang browser hijacker. Arctic Wolf tracks three new campaigns.

A new GST phishing campaign targets Indian taxpayers. This operation delivers Remcos RAT malware using an embedded bitmap payload to steal user credentials.
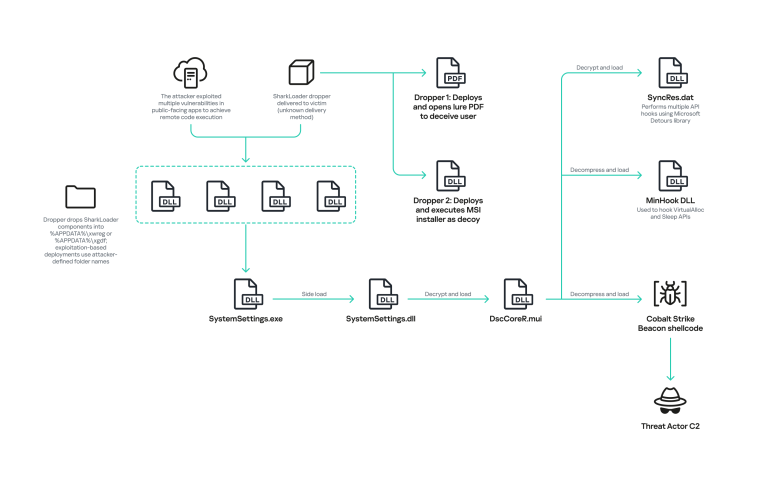
Kaspersky details SharkLoader malware, which deploys Cobalt Strike Beacon in the global StrikeShark campaign via DLL sideloading and exploited apps.

The OXLOADER malware loader spreads via malicious Google Ads, dropping the CASTLESTEALER infostealer with heavy obfuscation and anti-VM checks.
A massive Conti ransomware guilty plea reveals how these devastating ransomware attacks extorted $150 million from thousands of global victims.
North Korea’s "Contagious Interview" campaign expands to 1,700+ malicious packages across npm, PyPI, and more. Learn how to protect your dev environment.
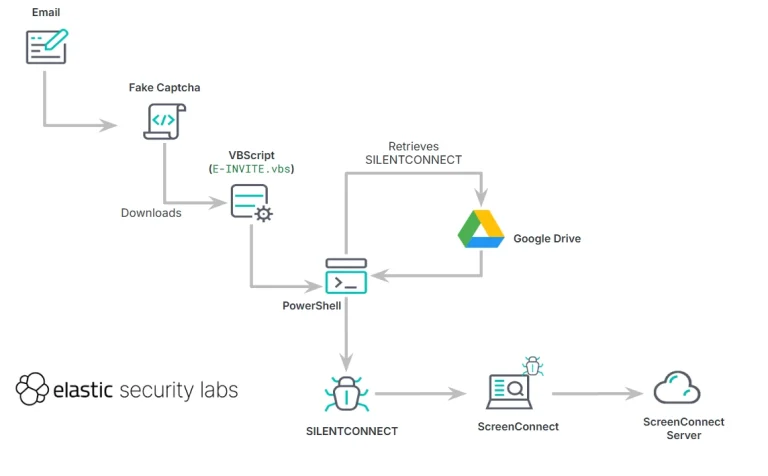
Elastic Security Labs uncovers SILENTCONNECT, a stealthy loader using Cloudflare and Google Drive to deliver RMM tools for "hands-on keyboard" attacks.
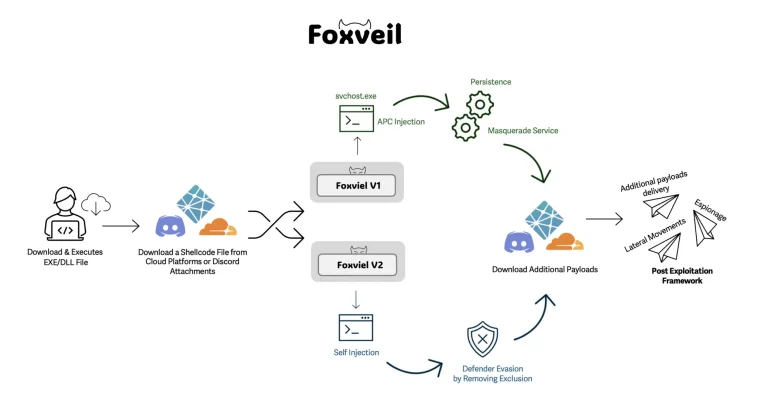
Cato CTRL discovers Foxveil, a new malware loader abusing Cloudflare, Netlify & Discord to bypass defenses. Active since Aug 2025. Learn the signs.

IIJ exposed a novel loader that simultaneously deploys TorNet (TOR C2) and PureHVNC (RAT) via DLL sideloading. It uses MurmurHash2 for API hashing and injects into jsc.exe for stealth.

A new malware loader, CountLoader, is linked to Russian ransomware groups. The malware uses phishing lures impersonating the Ukrainian National Police to deliver payloads.

A new report reveals HijackLoader, a Malware-as-a-Service loader. It uses advanced evasion and anti-analysis techniques to deliver stealers and other payloads.

Zscaler reveals TransferLoader: a stealthy malware using IPFS and obfuscation to drop ransomware and backdoors. A new threat in the wild since 2025.

Darktrace uncovers a SocGholish campaign using obfuscated loaders and legacy Windows exploits to harvest NTLM hashes and deliver ransomware payloads.
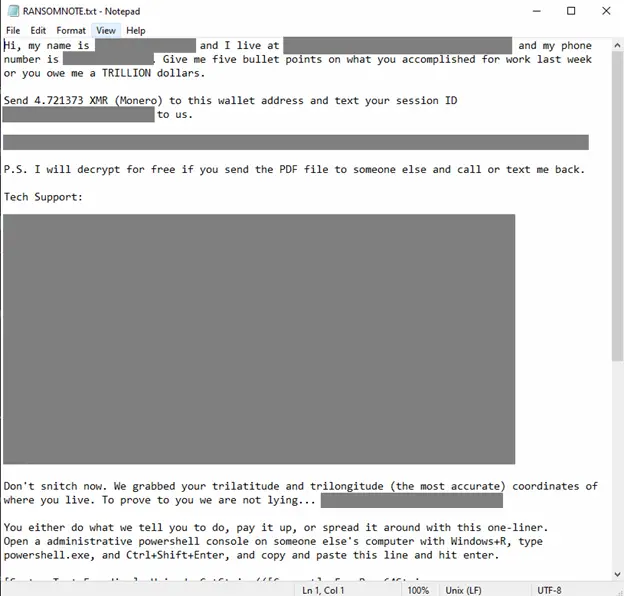
FOG ransomware campaign spreads via phishing and stealthy loaders, targeting tech, education, and manufacturing sectors with obfuscated payloads.