 Do Son
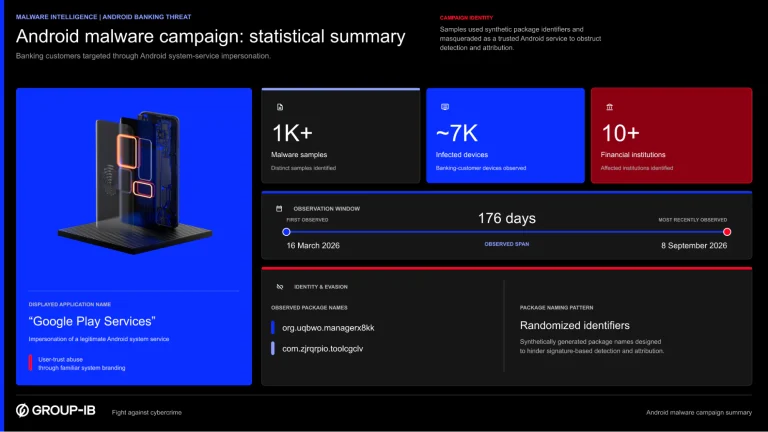
The Mirax Android RAT, a device takeover malware posing as Google Play Services, has infected thousands of phones to drain META bank accounts.
Mobile Banking Fraud
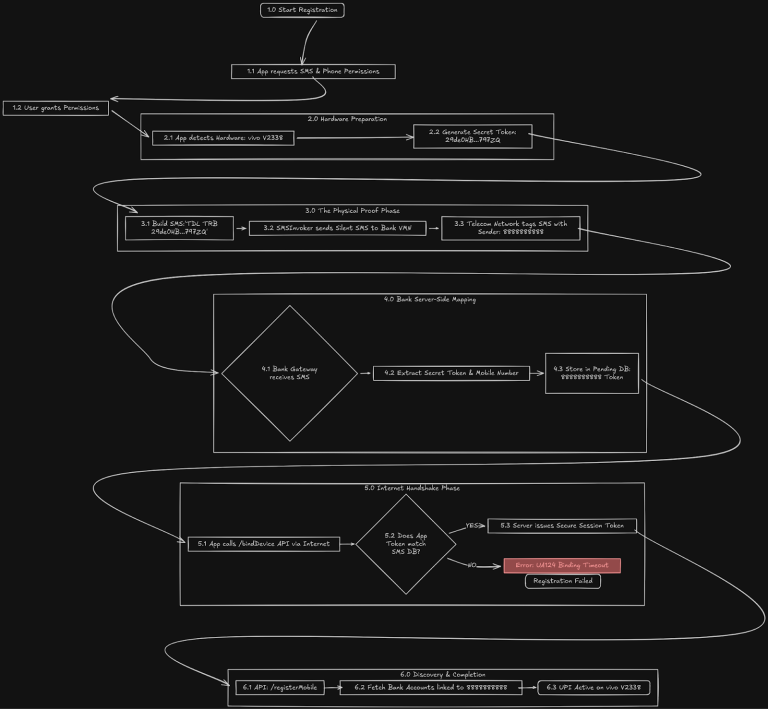
CloudSEK reveals how attackers use LSPosed and the "Digital Lutera" module to bypass Android UPI SIM-binding, gaslighting payment apps for remote fraud.

Group-IB exposes an industrialized mobile banking fraud campaign in Indonesia. GoldFactory hackers use fake Coretax apps and Gigabud.RAT to drain accounts.
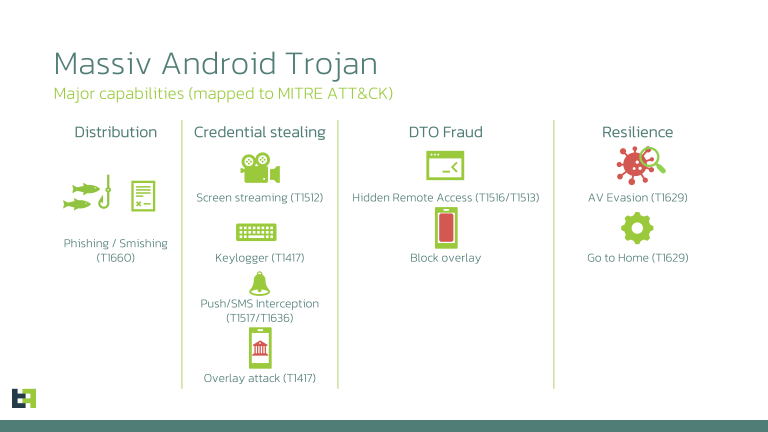
ThreatFabric exposes Massiv, a new Android banking Trojan hiding in fake IPTV apps. The malware uses accessibility permissions for full device takeover.