
 Do Son
Rapid7 unmasks Iranian APT MuddyWater using a Chaos ransomware "false flag" to hide state-sponsored espionage. See how they bypassed MFA via MS Teams.
MOIS

The US DOJ has seized four domains used by Iran's MOIS to orchestrate global cyberwarfare, doxing, and death threats against dissidents and governments.
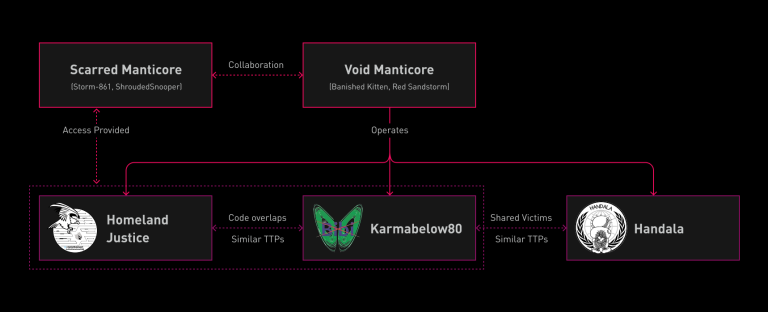
Check Point Research unmasks Handala Hack (Void Manticore), an Iranian MOIS threat actor using AI scripts and NetBird for destructive wiping attacks.