
 Do Son
n8n fixes three critical 9.4 CVSS flaws (CVE-2026-44790/91/89). Authenticated users can break sandboxes for local file read and server-level RCE. Patch now!
n8n
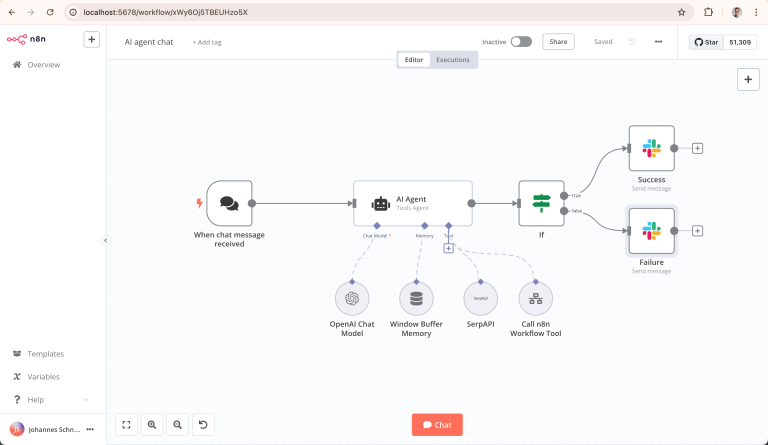
Critical CVSS 10 and 9.4 vulnerabilities hit n8n. Prototype pollution in XML nodes can lead to full RCE. Patch to v2.18.1 or v1.123.32 immediately.
n8n patches critical 9.4 CVSS RCE flaws in Merge and GSuiteAdmin nodes. Attackers can hijack servers via SQL sandbox escapes or prototype pollution. Update now!
CISA warns of a critical 10.0 CVSS RCE flaw (CVE-2025-68613) in n8n workflow automation. Update to version 1.122.0 immediately to prevent server takeover.
n8n patches three critical 9.4 CVSS vulnerabilities (CVE-2026-27497, 27577, 27495) allowing remote code execution via Merge nodes and sandboxes. Update now!
Critical n8n flaws (CVE-2026-25053, 25056) allow attackers to hijack servers via Git & Merge nodes. Update to v2.5.0 now to prevent RCE.
Critical n8n RCE (CVE-2026-1470) lets attackers bypass sandbox defenses via malicious expressions. CVSS 9.9. Check versions 1.123.17 & 2.x now.

Alert: Public exploit released for n8n CVE-2026-21858 (CVSS 10.0). Unauthenticated attackers can seize full control. Update to v1.121.0 now.
Urgent: n8n CVE-2026-21877 (CVSS 10.0) allows full server compromise via Git node. Update to v1.121.3 now to prevent RCE and arbitrary file writes.

CVE-2025-68668: A critical n8n flaw lets attackers escape the Python sandbox for full RCE. Learn how this bridge failure leads to total system compromise.
n8n warns of a CVSS 10.0 RCE (CVE-2025-68613) in its expression system. Attackers can seize total server control. Upgrade to v1.122.0 immediately.
A Critical RCE flaw (CVSS 9.4) in the n8n Git Node allows command execution by manipulating the core.hooksPath setting in workflows. Update to v1.119.2 immediately.