
 Do Son
Zscaler reveals a 2026 attack chain using fake Adobe Reader lures to install ScreenConnect via in-memory execution and UAC bypass. Protect your network now!
.NET Reflection
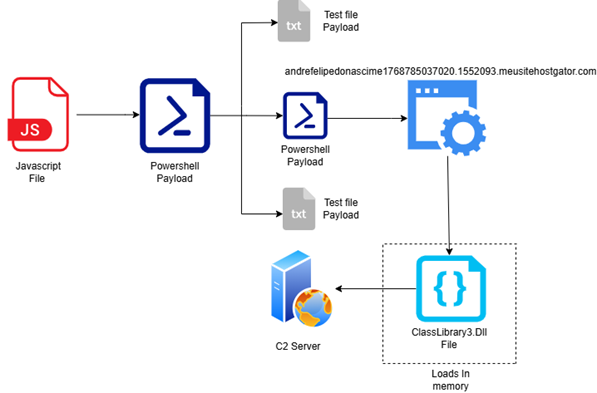
Lat61 Team uncovers DesckVB RAT, a stealthy 2026 Trojan using in-memory .NET loaders & JS obfuscation to hijack systems and evade AV. Learn how it works.