 Do Son
Critical Citrix NetScaler vulnerability CVE-2026-107406 (CVSS 9.5) can lead to RCE on SAML-configured ADC and Gateway. Upgrade now.
NetScaler ADC
CVE-2026-19490 (CVSS 9.3) is a critical NetScaler authentication bypass in NetScaler Gateway and ADC. Patch now to block unauthenticated access.
Six NetScaler vulnerabilities allow denial of service, memory overreads, and an unauthenticated file read. Patch NetScaler ADC and Gateway now.
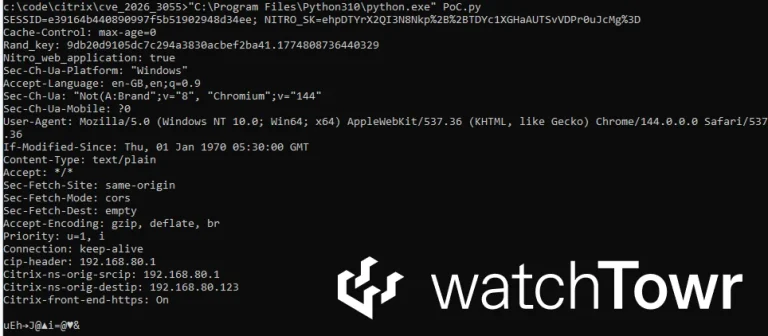
CISA adds Citrix NetScaler CVE-2026-3055 to KEV. This 9.3 CVSS flaw "bleeds" admin sessions via SAML. Federal agencies must patch by April 2, 2026.

Find out about the critical vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway. CVE-2024-8534 and CVE-2024-8535 may lead to service interruptions and unauthorized access.
CVE-2023-6548, a vulnerability involving improper control of code generation ('Code Injection'), was initially disclosed by Citrix

Cloud Software Group has issued a security advisory warning customers of a critical vulnerability (CVE-2024-6387) in OpenSSH

Citrix has sounded an alarm for its customers regarding two critical zero-day vulnerabilities, CVE-2023-6548 and CVE-2023-6549