 Do Son
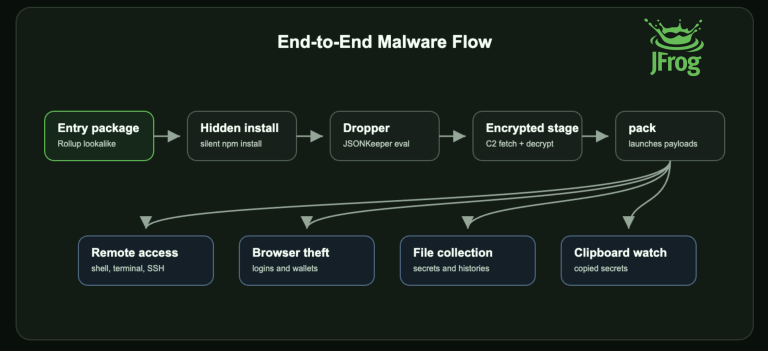
New Lazarus npm malware masquerades as Rollup polyfills, hiding remote-access and wallet-theft payloads. JFrog uncovered six malicious packages.
npm malware

A malicious unscoped "tanstack" npm package used live-debugged postinstall scripts to steal .env secrets via Svix webhooks. Check your dependencies now.

ReversingLabs uncovers PromptMink: A DPRK campaign using LLM-generated npm packages to trick AI coding agents into installing crypto-stealing malware.
SAP developers are under attack. A surgical credential stealer hijacks CI/CD runners and cloud tokens via npm preinstall hooks. Rotate all secrets immediately.
North Korean hackers are now targeting AI tools like Cursor and Claude. The OtterCookie malware steals API keys and conversation logs. Is your dev environment safe?

StepSecurity uncovers a supply chain attack where a verified GitHub org, dev-protocol, was hijacked to spread malicious Polymarket bots and steal crypto.

Tenable uncovers "ambar-src," a malicious npm package mimicking "ember-source." It uses preinstall scripts to deploy reverse shells and Apfell malware.

Critical dYdX supply chain attack: Compromised npm & PyPI packages steal seed phrases & deploy RATs. Remove @dydxprotocol/v4-client-js immediately.

Malicious npm package "ansi-universal-ui" drops "G_Wagon" infostealer to steal cloud keys and wallets. Check for .gwagon_status and rotate creds now.

Aikido discovers a Remote Access Trojan (RAT) hidden in rand-user-agent, a popular npm package with 45,000 weekly downloads.

A fake npm package named pdf-to-office has been discovered injecting malicious code into Atomic and Exodus crypto wallets, redirecting funds and stealing data