
 Do Son
A distributed npm supply chain attack dropped a cross-platform RAT on Alibaba developers. Socket found malicious npm packages hiding loader code.
npm Supply Chain Attack
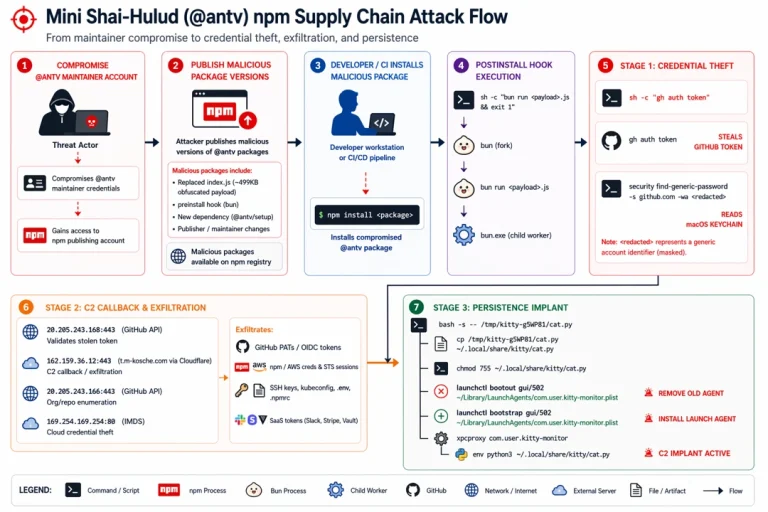
Microsoft warns of an aggressive Mini Shai-Hulud worm attack targeting the @antv npm ecosystem and stealing secrets from cloud-connected CI/CD pipelines.

TeamPCP has open-sourced the Shai-Hulud supply chain worm. Multiple malicious typosquatted NPM packages are already weaponizing the AI-synthesized code.

OpenAI rotates code signing certificates following the TanStack npm breach. macOS users must update ChatGPT and Codex manually before June 12, 2026.
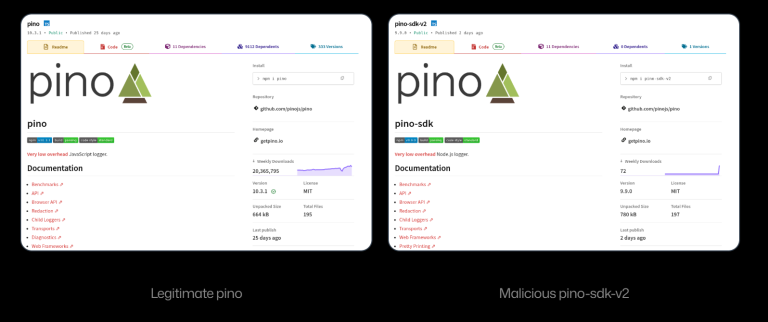
SafeDep uncovers pino-sdk-v2, a malicious npm package impersonating the pino logger to silently steal .env secrets and exfiltrate them via Discord.