 Do Son
Four OpenAM vulnerabilities are fixed in 16.1.2. CVE-2026-62379 (CVSS 9.8) allows unauthenticated remote code execution; CVE-2026-62261 scores 9.9.
OpenAM

A critical OpenAM WebAuthn RCE flaw (CVE-2026-45051) allows code execution via Java deserialization. Update OpenAM to 16.1.1 to stay protected.
Critical 9.3 RCE in OpenAM (CVE-2026-33439) allows unauthenticated attackers to execute OS commands via jato.clientSession. Patch your 16.0.5 servers now!
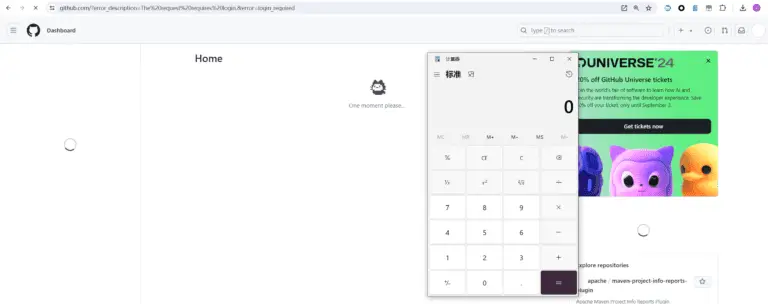
Explore the severe security vulnerability, CVE-2024-41667, in OpenAM. Understand the risks it poses and the potential consequences for organizations.