 Do Son
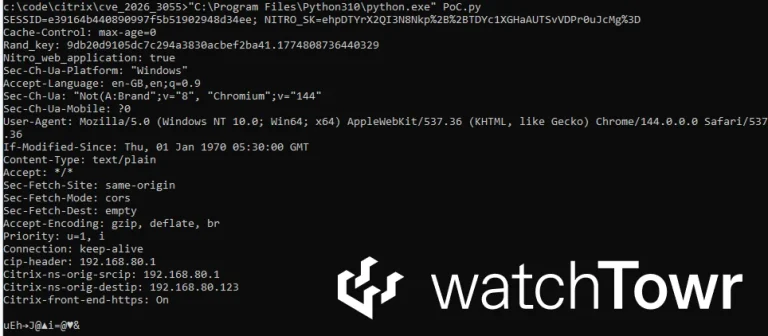
CISA adds Citrix NetScaler CVE-2026-3055 to KEV. This 9.3 CVSS flaw "bleeds" admin sessions via SAML. Federal agencies must patch by April 2, 2026.
out-of-bounds read

Google releases Chrome v145.0.7632.116 to patch high-severity flaws in Media, DevTools, and the Tint graphics engine. Update now to prevent memory leaks.

CISA adds critical CitrixBleed 2 (CVE-2025-5777, CVSS 9.2) to KEV, confirming active exploitation. Attackers are extracting session tokens to bypass MFA and hijack sessions on NetScaler ADC/Gateway

Citrix Bleed 2 (CVE-2025-5777, CVSS 9.2) is actively exploited to hijack sessions and bypass MFA on NetScaler ADC/Gateway. Patch immediately to prevent covert access and data theft.
Discover the critical vulnerabilities in KSMBD, CVE-2024-56626 and CVE-2024-56627, that could allow attackers to gain control of Linux systems.