 Do Son
PHP is proposing a shift to the 3-Clause BSD License for PHP 9.0, aiming to resolve long-standing compatibility issues and streamline its open-source framework.
php

A critical SSTI flaw (CVE-2025-53833, CVSS 10.0) in LaRecipe allows unauthenticated RCE on affected servers via template injection. Update to v2.8.1 immediately!
Interlock RAT Gets PHP Makeover: New Variant Uses Steganography & ClickFix for Stealthy Infiltration

Interlock RAT Gets PHP Makeover: New Variant Uses Steganography & ClickFix for Stealthy Infiltration
The DFIR Report uncovers a new PHP-coded Interlock RAT variant, using compromised websites and ClickFix social engineering to deploy stealthy malware for recon and persistence.
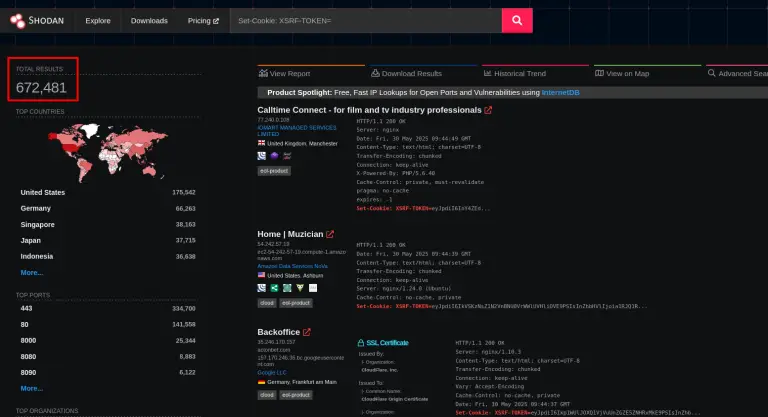
Synacktiv reveals Laravel’s APP_KEY vulnerability allows RCE via deserialization attacks when the key is leaked or guessable, risking full application compromise.

PHP patches two flaws: CVE-2025-1735 allows SQL injection/crashes in pgsql, and CVE-2025-6491 enables DoS in SOAP via oversized XML. Update immediately!

A critical flaw (CVE-2025-52562, CVSS 10.0) in Convoy KVM panel allows unauthenticated remote code execution via directory traversal.

Explore a critical vBulletin RCE vulnerability stemming from a flawed patch. This article details the PHP Object Injection leading to RCE, complete with a PoC

A critical Auth0 PHP SDK deserialization flaw (CVE-2025-48951, CVSS 9.3) allows unauthenticated RCE in web apps. Patch to v8.14.0+ immediately!

Roundcube Webmail has patched a critical RCE vulnerability (CVE-2025-49113) allowing remote code execution post-authentication. Update to 1.6.2 or 1.5.10 immediately!

A critical pre-authentication RCE vulnerability in vBulletin 5.x and 6.x allows full server compromise. A PoC exploit is available.

Critical vulnerability (CVSS 9.1) in Auth0-PHP SDK! This flaw threatens applications with over 16 million downloads. Update now to avoid brute force attacks.

CVE-2024-58136: A security vulnerability in the Yii 2 PHP framework is being actively exploited. Learn about the risk and necessary updates.

Explore the latest PHP vulnerabilities and their implications for web security. Stay informed to protect your applications.

Learn about CVE-2025-27517, a critical remote code execution vulnerability affecting Volt that poses significant security risks.

Learn about CVE-2022-31631 and its risks related to SQL injection in PHP. Update your PHP to stay secure from vulnerabilities.
Learn about the critical vulnerabilities in PHP versions prior to 8.1.31, 8.2.26, and 8.3.14. CVE-2024-8932 enables attackers to execute arbitrary code.

Learn about CVE-2024-47823, a critical vulnerability in Livewire framework for Laravel, allowing remote code execution via file uploads.

Critical security vulnerabilities discovered in Scriptcase! Update now to protect your applications from potential remote code execution.
Stay updated on the latest PHP vulnerability advisory. Learn about the potential log tampering, file inclusion, and data integrity violations.

Uncover Backdoor.Msupedge, a sophisticated malware found in a recent cyberattack. Learn how it uses DNS tunneling for its covert communication.
Mitel has issued two critical security advisories warning users of a severe vulnerability in the PHP scripting engine
A critical vulnerability in PHP, designated CVE-2024-4577, has become a prime target for cybercriminals within a day of its public disclosure