 Do Son
Upgrade to Composer 2.11.0 or 2.2.31 to fix two Composer vulnerabilities: path traversal GHSA-c968-33g3-wh7p and token leak GHSA-fm2w-xgf2-f9fh.
php
CISA adds PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 to the CISA KEV catalog after confirmed RCE and suspected DPRK-linked scanning.
OpenMage fixes 34 OpenMage vulnerabilities in Magento LTS, including a critical CSRF flaw that hands out API tokens. Upgrade to 20.19.0 or 20.18.2.
PHP2Shell affected products list: vendor patch status for CVE-2026-109618 and CVE-2026-109619 across PAN-OS, QNAP, Cisco, Citrix, F5 and more.
PHP warns of CVE-2026-115560, a PHP session vulnerability that follows PHP2Shell. Disable session.upload_progress until the next bugfix release.
A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.
PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now.
PHP fixes two critical PHP RCE vulnerabilities, CVE-2026-109618 and CVE-2026-109619, allowing remote code execution. Update to 8.5.12 or 8.4.27.
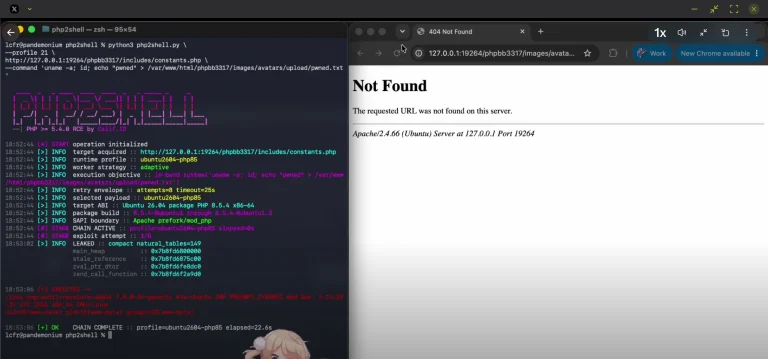
Cloudflare reports early attacks on two critical PHP flaws ahead of the PHP security release fixing remote code execution bugs CVE-2026-109618.
A critical Laravel authentication bypass (CVSS 9.2) in TokenGuard enables account takeover without a token. Upgrade to 13.29.0 or 12.68.0.
The PHP project patched critical PHP vulnerabilities across multiple branches. Update now to resolve these PHP vulnerabilities and secure your web servers.
A PHP SQL injection flaw, CVE-2026-17543, was patched alongside two memory bugs. Update to PHP 8.2.33, 8.3.33, 8.4.24, or 8.5.9 now.

Two PHP flaws are patched. CVE-2026-12184 is a PHP remote DoS that crashes PHP-FPM, and CVE-2026-14355 causes memory corruption. Update PHP now.

A critical PhpSpreadsheet RCE vulnerability impacts 312 million users. Learn how the CVE-2026-45034 exploit bypasses patches and triggers code execution.

Composer CVE-2026-45793 leaks GitHub tokens into CI/CD logs due to a validation error. Update to version 2.9.8 now and audit your GitHub Action logs.
PHP releases urgent security patches for a 9.5 severity RCE in the SOAP extension and a PHP-FPM XSS flaw. Update to 8.2.31, 8.3.31, 8.4.21, or 8.5.6 now!
North Korea’s "Contagious Interview" campaign expands to 1,700+ malicious packages across npm, PyPI, and more. Learn how to protect your dev environment.

Synacktiv exposed a critical flaw chain in Snipe-IT. A low-privileged user can exploit a Stored XSS (CVE-2025-59712) to hijack admin sessions and trigger RCE (CVE-2025-59713) via unsafe deserialization.
A new report reveals a critical SSRF vulnerability in the PhpSpreadsheet library. The flaw could allow attackers to access internal networks and sensitive data.

A critical SQL injection flaw (CVE-2025-54119, CVSS 10.0) in ADOdb’s SQLite3 driver allows arbitrary SQL execution via improperly escaped table names.

A critical command injection flaw (CVE-2025-54418, CVSS 9.8) in CodeIgniter's ImageMagick handler allows remote code execution via malicious filenames or text.

A critical RCE (CVE-2025-54068) in Livewire v3.6.3 and earlier allows unauthenticated attackers to execute arbitrary code on millions of Laravel applications. Update now!