 Do Son
Two critical Portainer vulnerabilities enable a bind mount bypass and Docker host takeover by standard users. Upgrade to Portainer 2.45.2 now.
Portainer
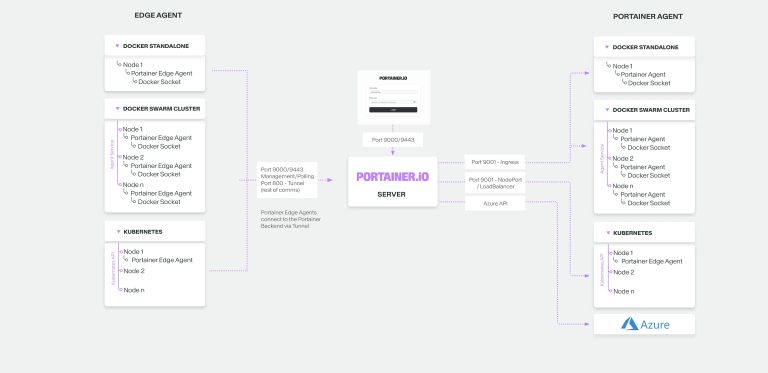
Portainer fixes two critical 9.4 CVSS flaws (CVE-2026-44848/49) allowing instant container escape to host root. Patch your environments now!

Fortinet exposed TruffleNet, a massive BEC campaign using stolen AWS keys to exploit Amazon SES for email fraud. It abuses Portainer as a C2 and uses TruffleHog for reconnaissance.