 Do Son
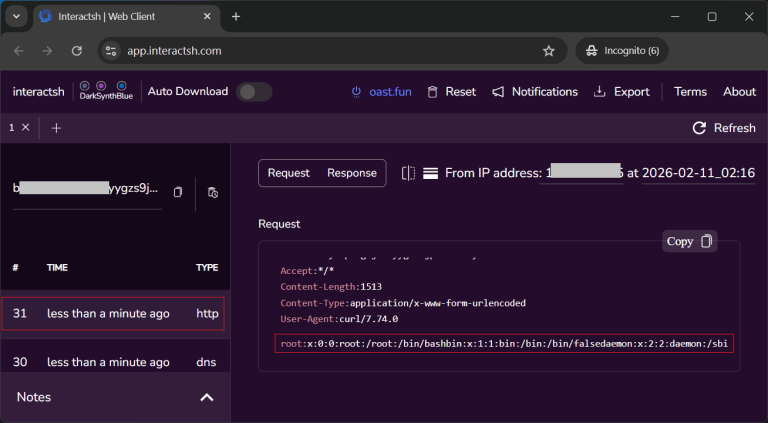
Arctic Wolf warns of CVE-2026-1731, a critical BeyondTrust flaw exploited in the wild. Attackers use it to deploy backdoors. Patch self-hosted instances now.
Privileged Remote Access

Critical BeyondTrust flaw CVE-2026-1731 (CVSS 9.9) allows unauthenticated RCE on Remote Support & PRA appliances. Update to v25.3.2 immediately.

BeyondTrust warns of a high-severity unauthenticated RCE flaw in Remote Support and PRA, exploitable via the built-in chat feature. Patch immediately

CVE-2025-0217 flaw in BeyondTrust PRA allows session hijacking via local auth bypass. Upgrade to version 25.1+ to prevent exploitation.
Protect your organization from critical command injection vulnerability CVE-2024-12356 in BeyondTrust’s Privileged Remote Access and Remote Support solutions.