 Do Son
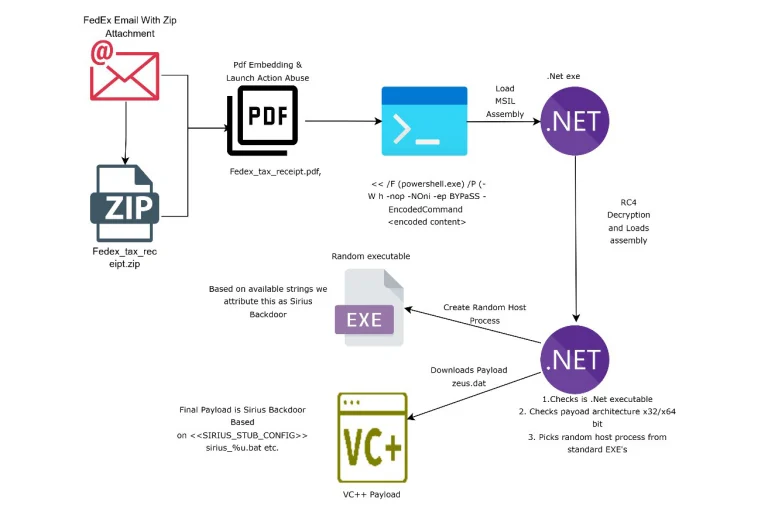
Trellix uncovers the Sirius Backdoor in fake FedEx tax invoices. See how the fileless Sirius Backdoor blinds EDRs and survives Windows OS resets.
Process Hollowing

Trellix details a DCRat campaign using SVG HTML smuggling and process hollowing to deploy DarkCrystal RAT via a Colombian judicial lure.
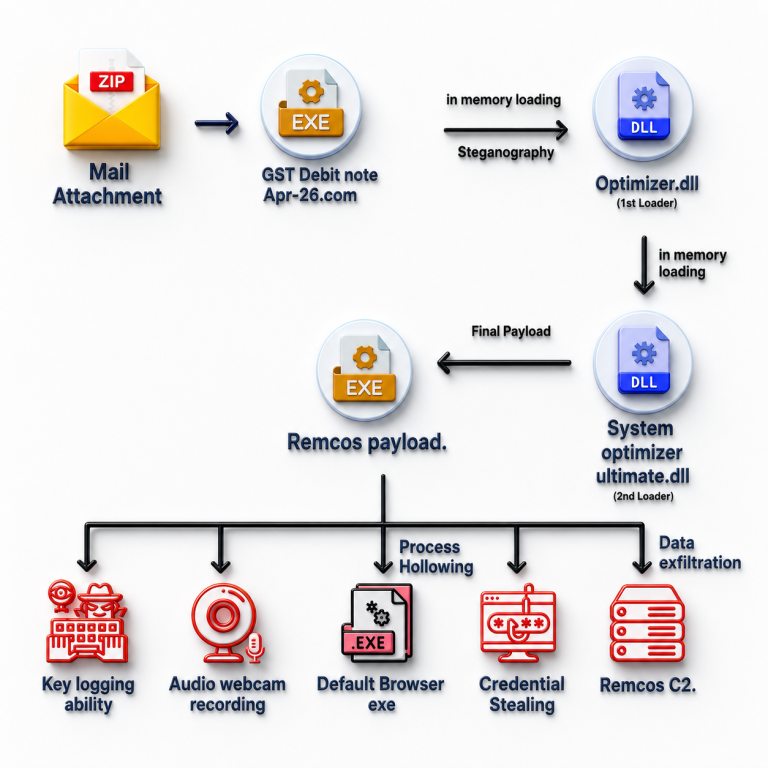
A steganographic loader hides Remcos RAT inside a bitmap and runs it in memory. K7 ties the fileless campaign to India via fake GST lures.

FortiGuard Labs uncovered AsyncRAT AI lures using fake AI guides and an AutoHotkey loader to inject a stealthy .NET RAT into memory.

A stealthy GPU cryptojacking campaign leverages AI search poisoning and process hollowing injection to hijack high-end rigs. Read the Microsoft report.

FortiGuard Labs exposes a highly evasive PureLogs info stealer campaign utilizing process hollowing and fileless execution.
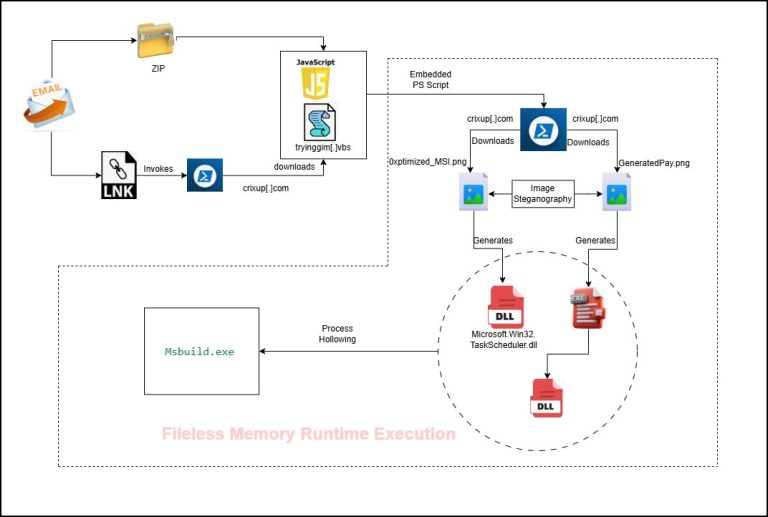
Trellix uncovers PureRAT, a modular Trojan hiding malware in PNG images. Learn how it uses steganography and fileless delivery to bypass Windows security.
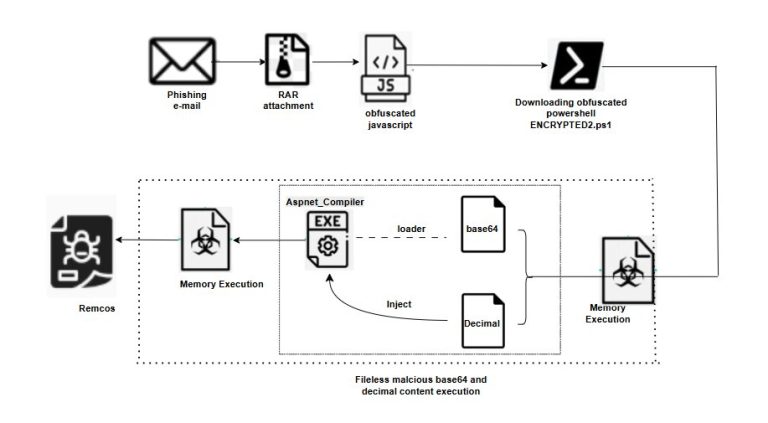
Trellix uncovers a stealthy, fileless Remcos RAT campaign utilizing process hollowing to execute entirely in memory and evade traditional security.

Phishing emails use malicious Excel files to deploy XWorm RAT. The fileless attack exploits CVE-2018-0802 to steal data & control systems.
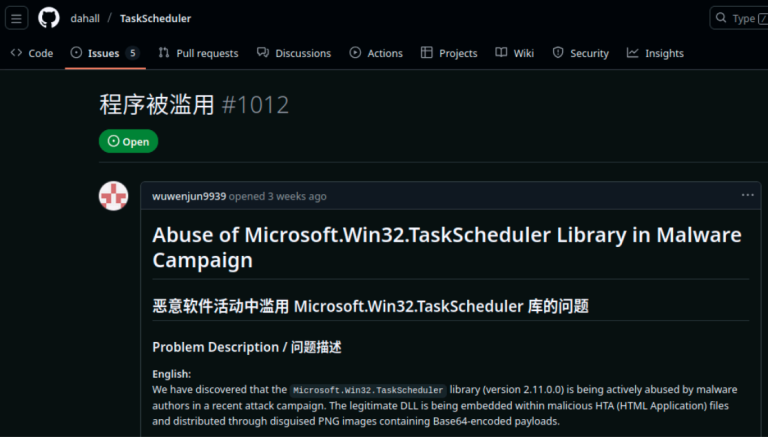
New "PhantomVAI" malware recycles old Hackforums "RunPE" code to bypass modern EDR. Campaigns use task scheduler masquerading to deliver infostealers.

Attackers use fake DHL invoices to sideload Phantom Stealer v3.5.0 via a signed Java utility. Malware hides in AddInProcess32.exe. Watch out.

New fileless Remcos RAT campaign uses a "[virus detected]" shipping lure to inject malware into memory via process hollowing. See how to spot it.

CloudSEK’s TRIAD unmasks Silver Fox APT, a China-linked group using Valley RAT to target India while hiding behind misattributed tax phishing lures.

A sophisticated Lumma Infostealer MaaS campaign targets users with pirated software installers. It uses NSIS/AutoIt scripts, Process Hollowing, and MEGA cloud to steal credentials from browsers and crypto wallets.

Unit 42 exposed PhantomVAI Loader, a stealthy MaaS tool that uses steganography (hiding DLL in images) and VM detection to deploy Katz Stealer in MSBuild.exe and exfiltrate crypto credentials globally.
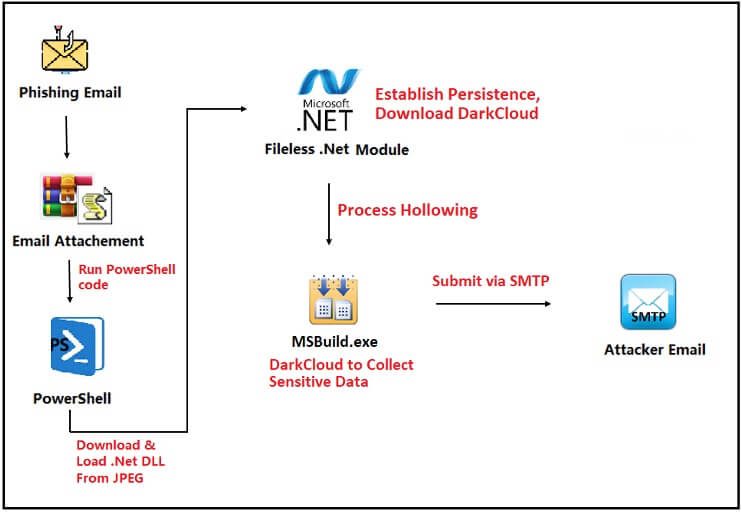
Fortinet uncovers a new DarkCloud stealer variant using a fileless, multi-stage attack chain with obfuscated PowerShell and process hollowing to evade detection and exfiltrate data.

Cyfirma reveals Raven Stealer, a new, lightweight MaaS infostealer built in Delphi/C++, using reflective process hollowing and Telegram bots for stealthy data exfiltration from browsers.

Katz Stealer is a dangerous MaaS info-stealer (starting at $100/month) that plunders digital identities, evades detection with stealthy techniques, and targets a vast array of sensitive data.

A new campaign uses encrypted VBScript (.VBE) to deploy a fileless Masslogger infostealer, which hides in the Windows Registry to steal credentials and evade antivirus.

Katz Stealer, a new stealthy MaaS, is actively stealing data from browsers, crypto wallets, and apps, using advanced evasion tactics like steganography and Discord hijacking.

A new phishing campaign delivers FormBook malware via Word docs, exploiting CVE-2017-11882. The fileless attack uses process hollowing to evade detection.
Uncover the details of a sophisticated phishing campaign distributing AsyncRAT and the Infostealer plugin. Learn how cybercriminals bypass security defenses and infiltrate victim systems.