
 Do Son
NVIDIA patches a critical 9.0 CVSS vulnerability (CVE-2025-33244) in the Apex library. Protect your AI models from RCE—upgrade to PyTorch 2.6+ now.
PyTorch
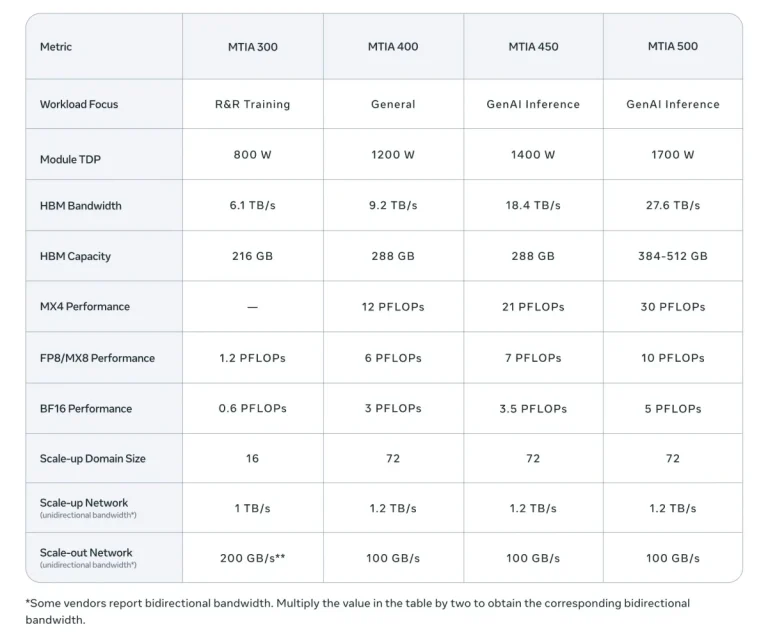
Meta shatters the industry standard with a 6-month chip cycle. Discover the MTIA 300-500 roadmap designed to slash AI costs and power 3 billion users by 2027.

PyTorch patches CVE-2026-24747 (CVSS 8.8). The "weights_only" safety flag failed, allowing RCE via malicious models. Update to v2.10.0 now.

NVIDIA at CES 2026: DGX Spark gets a 2.5× speed boost, Nsight Copilot for offline CUDA coding, and 8× faster video gen for MacBook Pro users.

A RCE flaw (CVE-2025-62164) in the vLLM inference engine allows attackers to crash servers or execute code by exploiting an out-of-bounds memory write via malicious prompt embeddings.

A Critical (CVSS 9.8) RCE flaw in Keras 3’s Torch backend (CVE-2025-49655) allows attackers to execute arbitrary code by loading a malicious model due to insecure deserialization.
CVE-2025-32434: Critical RCE vulnerability in PyTorch’s torch.load(weights_only=True) affects ≤2.5.1. Update to v2.6.0 to patch this major flaw