 Do Son
Acronis analyzes Qilin ransomware after 900+ attacks in 2026. See how ESXi Qilin ransomware scripts hijack VMware hosts and leak data on WikiLeaksV2.
Qilin Ransomware
Ransomware gangs exploit CVE-2026-0257, a GlobalProtect authentication bypass in PAN-OS, to slip past MFA and open VPN sessions. Patch now.
Arctic Wolf links Qilin ransomware attacks to CVE-2026-0257, a Palo Alto GlobalProtect auth bypass used for initial access. Patch PAN-OS now.

A critical Check Point VPN vulnerability is actively exploited in the wild, allowing unauthenticated attackers to bypass user login requirements.
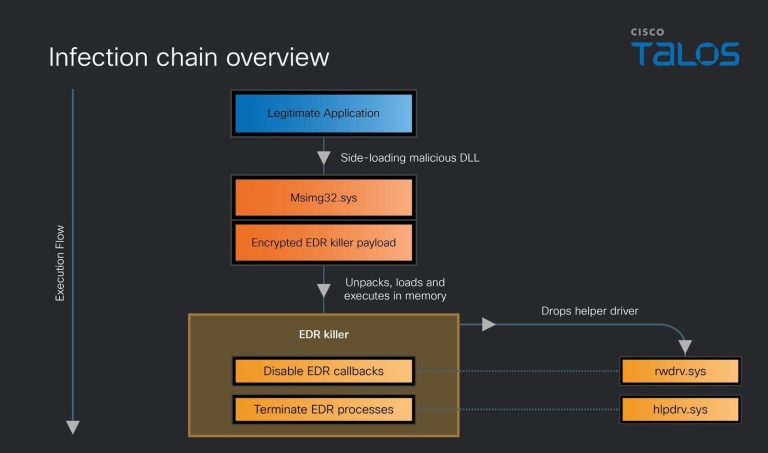
Cisco Talos unmasks a Qilin ransomware payload that terminates 300+ EDR drivers and manipulates the Windows kernel. See how this "EDR Killer" stays invisible.

Sophos CTU reveals how the ClickFix tactic led to a Qilin ransomware attack via NetSupport RAT and StealC V2 using stolen VPN credentials.

Cisco Talos reports Qilin RaaS is one of 2025’s biggest threats (40+ victims/month), abusing Cyberduck and Backblaze for data exfiltration and exploiting WDigest to steal admin passwords.

Resecurity exposed Qilin RaaS's reliance on bulletproof hosting (BPH) in Russia/HK. The same network was linked to the Asahi Group Holdings ransomware attack that stole 27 GB of data.

Cisco Talos' Q2 2025 report reveals phishing is the top access method. Ransomware, including Qilin, dominated, with a surprising trend of attackers abusing PowerShell 1.0 to evade security.

Learn about the Qilin ransomware attack that compromised an MSP and affected numerous customers through a phishing campaign.

Find out how the Qilin ransomware group is using a new approach to steal credentials from Google Chrome. Stay vigilant and protect your data.

Promises2Kids falls victim to Qilin Ransomware attack. Learn about the notorious hacker group and their double extortion tactics.